The Enterprise AI Control Plane
Decouple credentials. Govern models. Enforce guardrails.
Centralize frontier and sovereign models into private workspaces with zero-code guardrails, multi-span observability, and sub-millisecond failover.
Key Governance
Traffic Routing
Telemetry Spans
KMS Enclave
Connect Every Foundation Model, Cloud Provider & Custom Endpoint
Infralo is never limited to a fixed vendor list. Route, govern, and failover across every commercial API, open-weight model, and any private HTTP endpoint or internal VPC host that speaks standard JSON.
Any model endpoint that implements /v1/chat/completions or /v1/embeddings
immediately inherits Infralo's virtual keys, semantic caching, and audit logging with zero adapters
needed.
Override standard endpoints to any IP (e.g. http://10.0.4.12:8000/v1). Ideal for proprietary
fine-tuned weights, internal enterprise gateways, or Hugging Face Text Generation Inference.
Route zero-egress traffic directly into on-prem vLLM, Ollama, Triton, or Kubernetes clusters within your private sovereign cloud without sending data over the public internet.
Introducing Infralo Control Plane
Watch the official launch video. 78 seconds on why enterprise AI operations require an isolated control layer for intelligent routing, hardware credential vaulting, and multi-span distributed tracing.
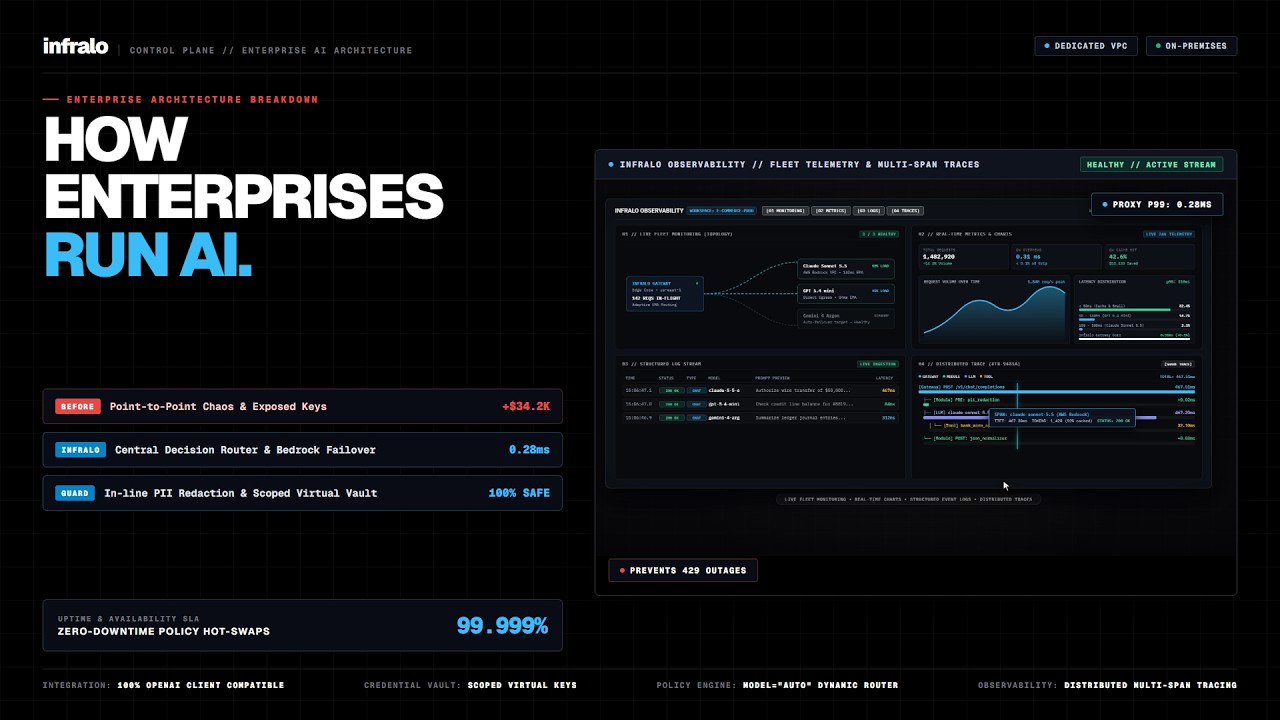
Beyond a Simple Gateway: The 3-Tier Control Plane
API proxies only forward tokens. Infralo delivers an isolated, three-tier control plane designed for enterprise compliance, tenancy boundaries, and zero-trust credential security.
Global Collection & Vault
Master provider credentials (OpenAI, Anthropic, Bedrock, Vertex) are encrypted with hardware KMS / HSM. Client apps and autonomous agents never see or hold raw provider keys.
- ✓ KMS-encrypted provider credentials
- ✓ Centralized vendor cost pooling
- ✓ Global rate limit & concurrency pools
Multi-Tenant Workspaces
Logical boundaries for enterprise teams, business units, or customer accounts. Issue scoped Virtual API
Keys (vk_...) with model whitelists, deployment scopes, and RBAC
roles.
- ✓ Cryptographic tenant boundaries
- ✓ Model & deployment whitelists
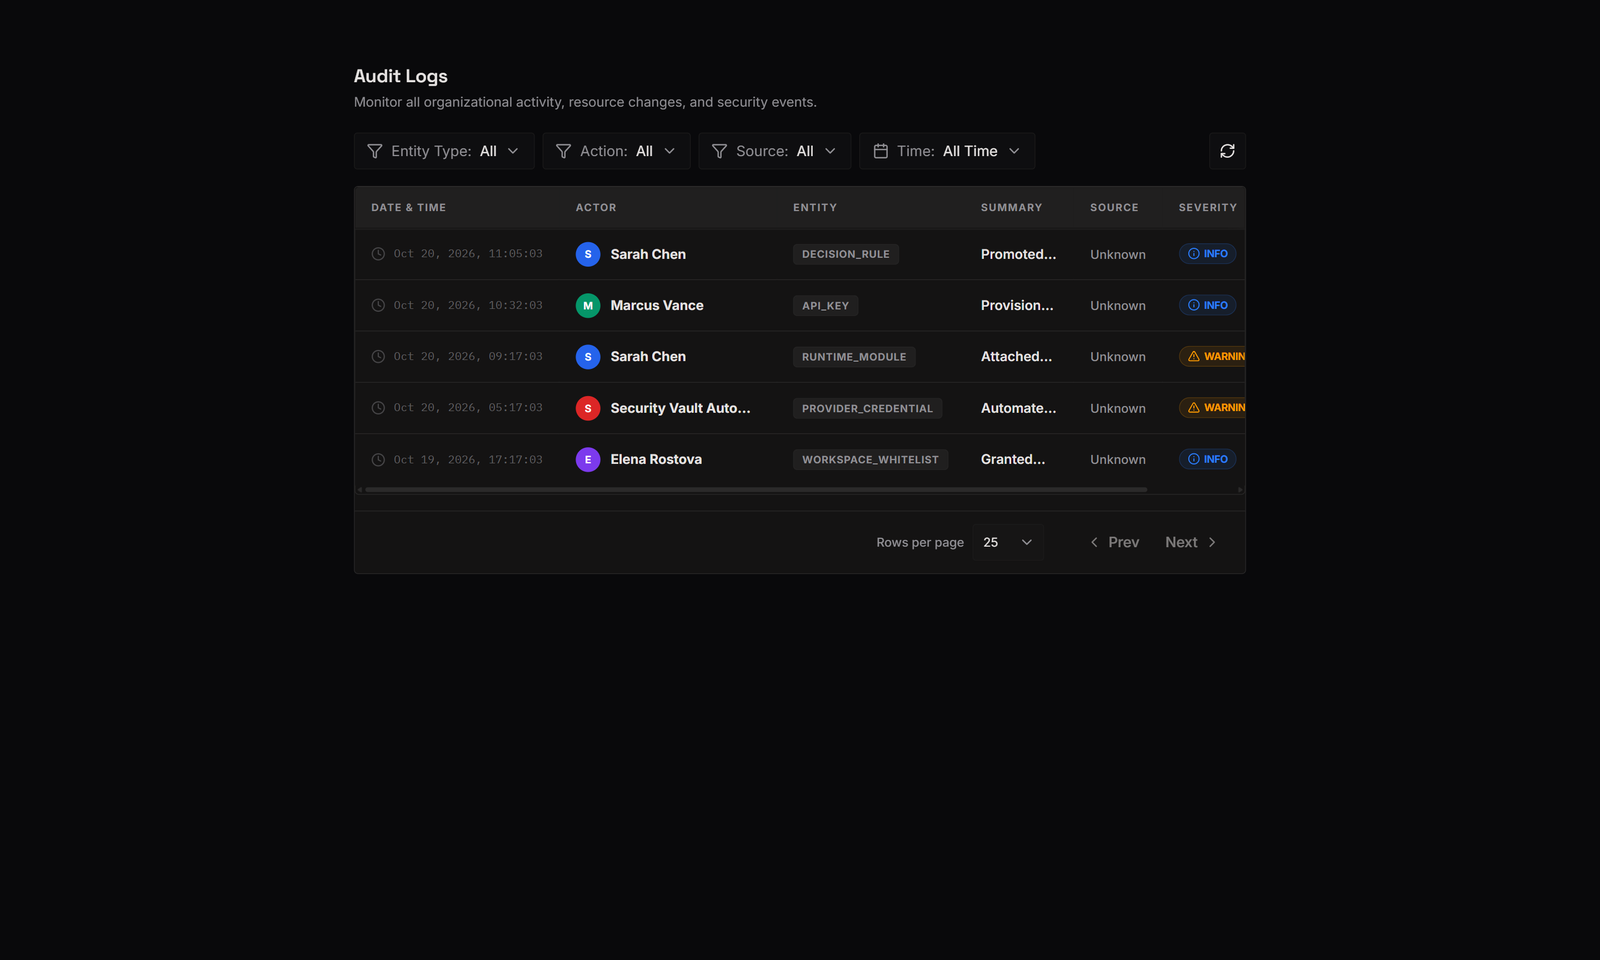
- ✓ Tamper-evident immutable audit logs
Virtual Deployments & Guardrails
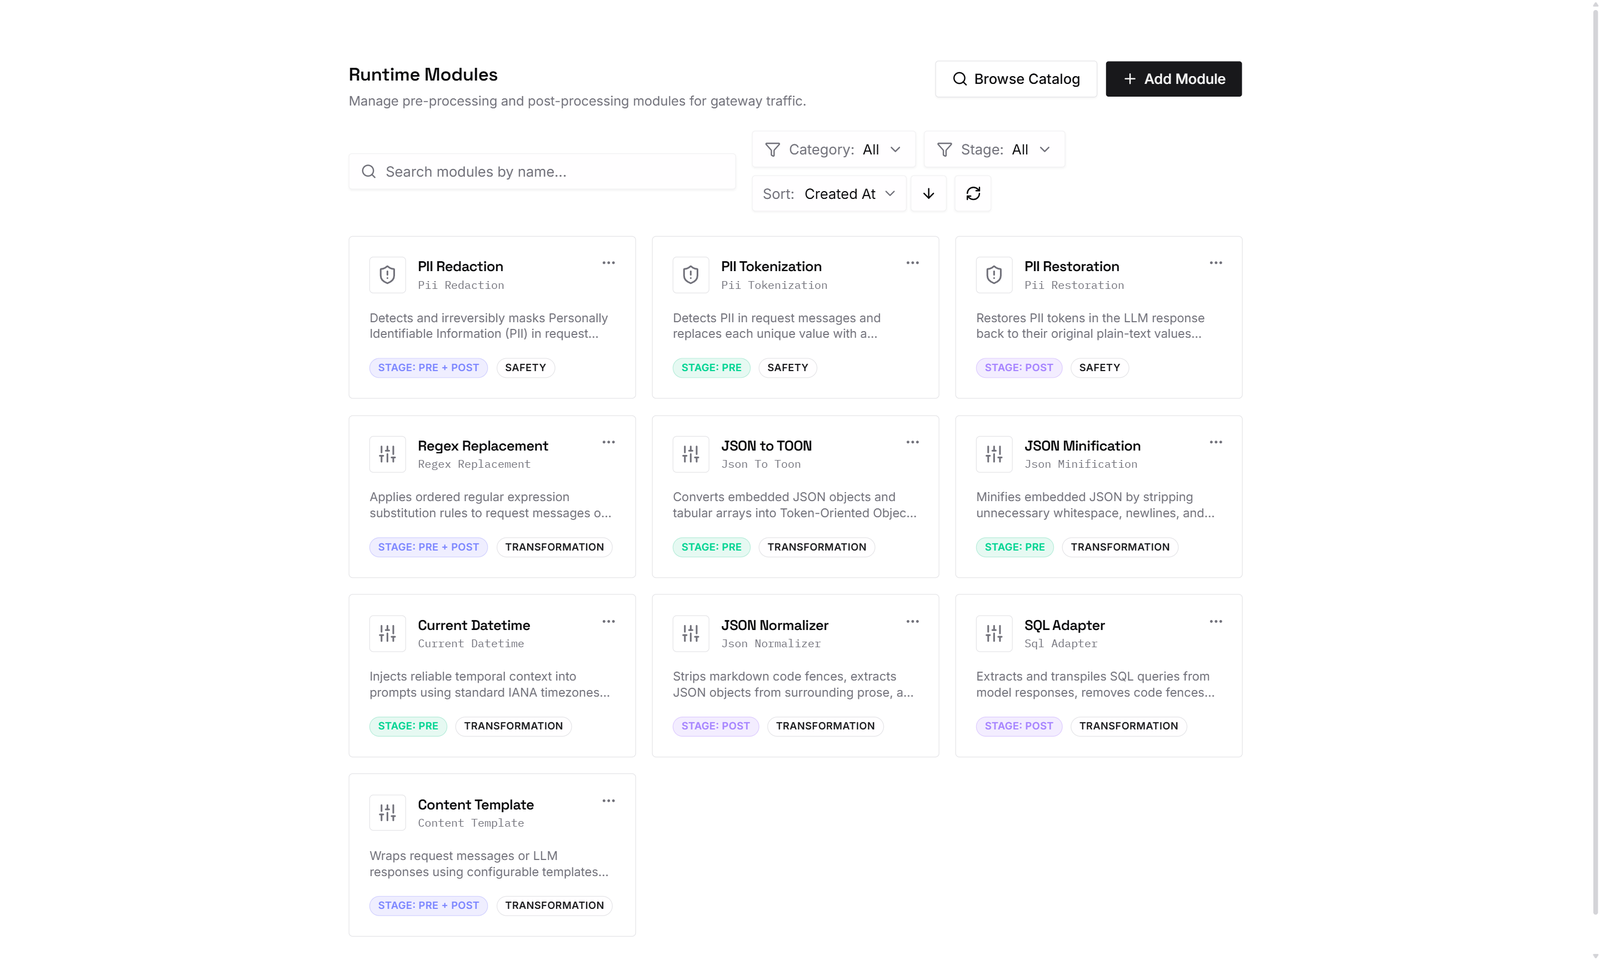
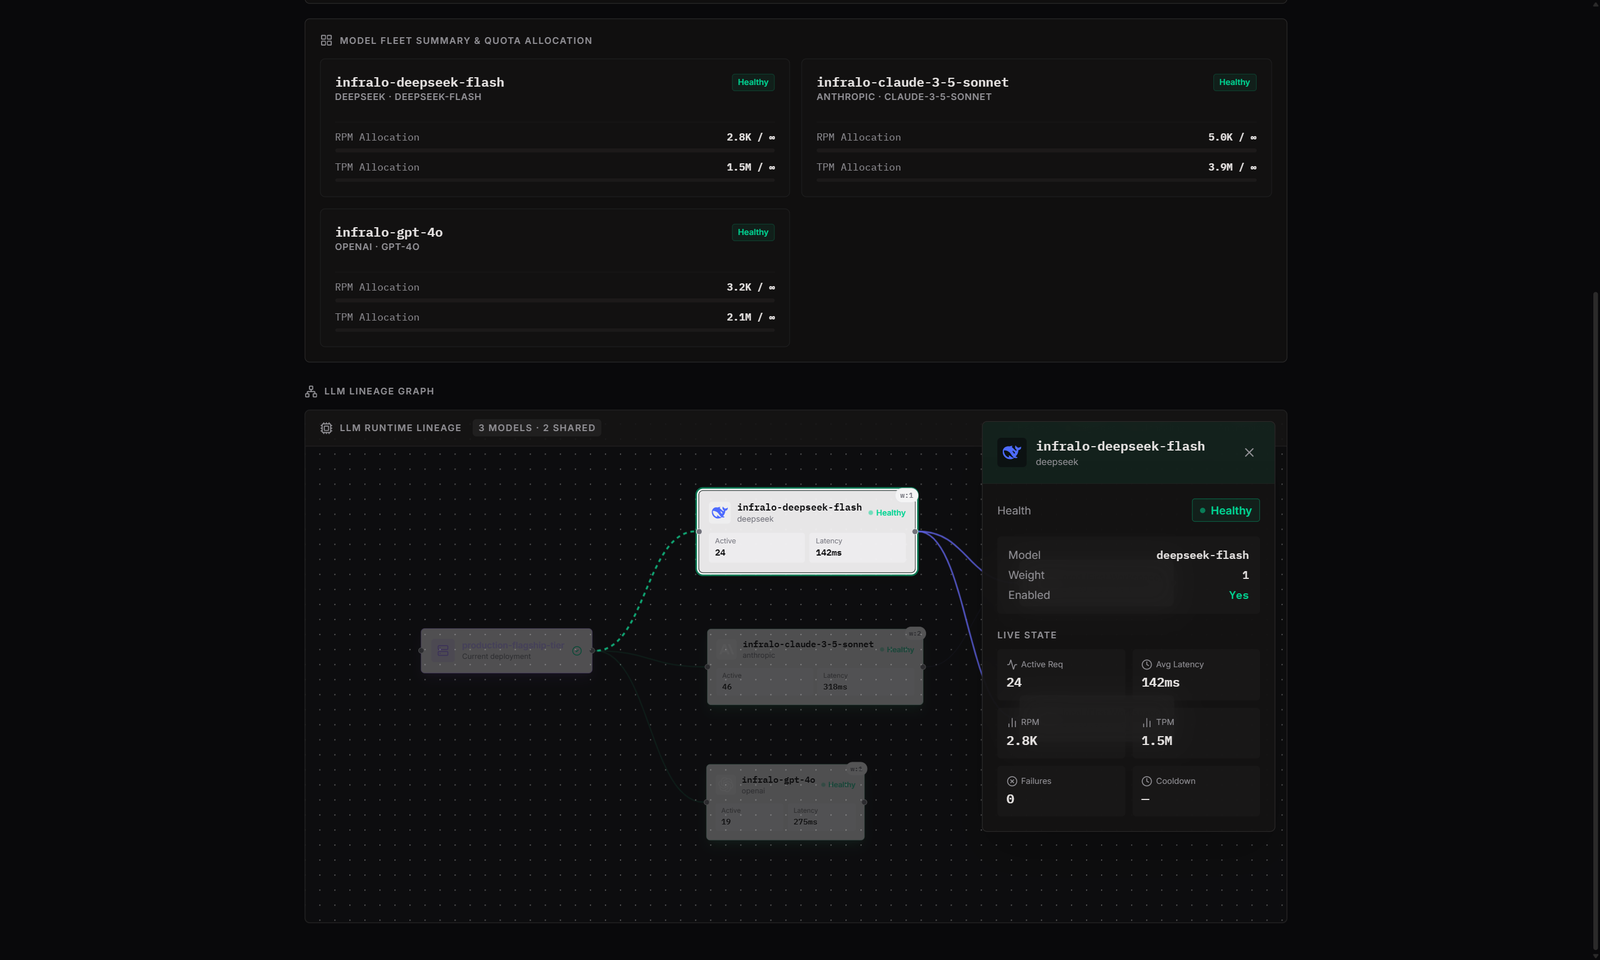
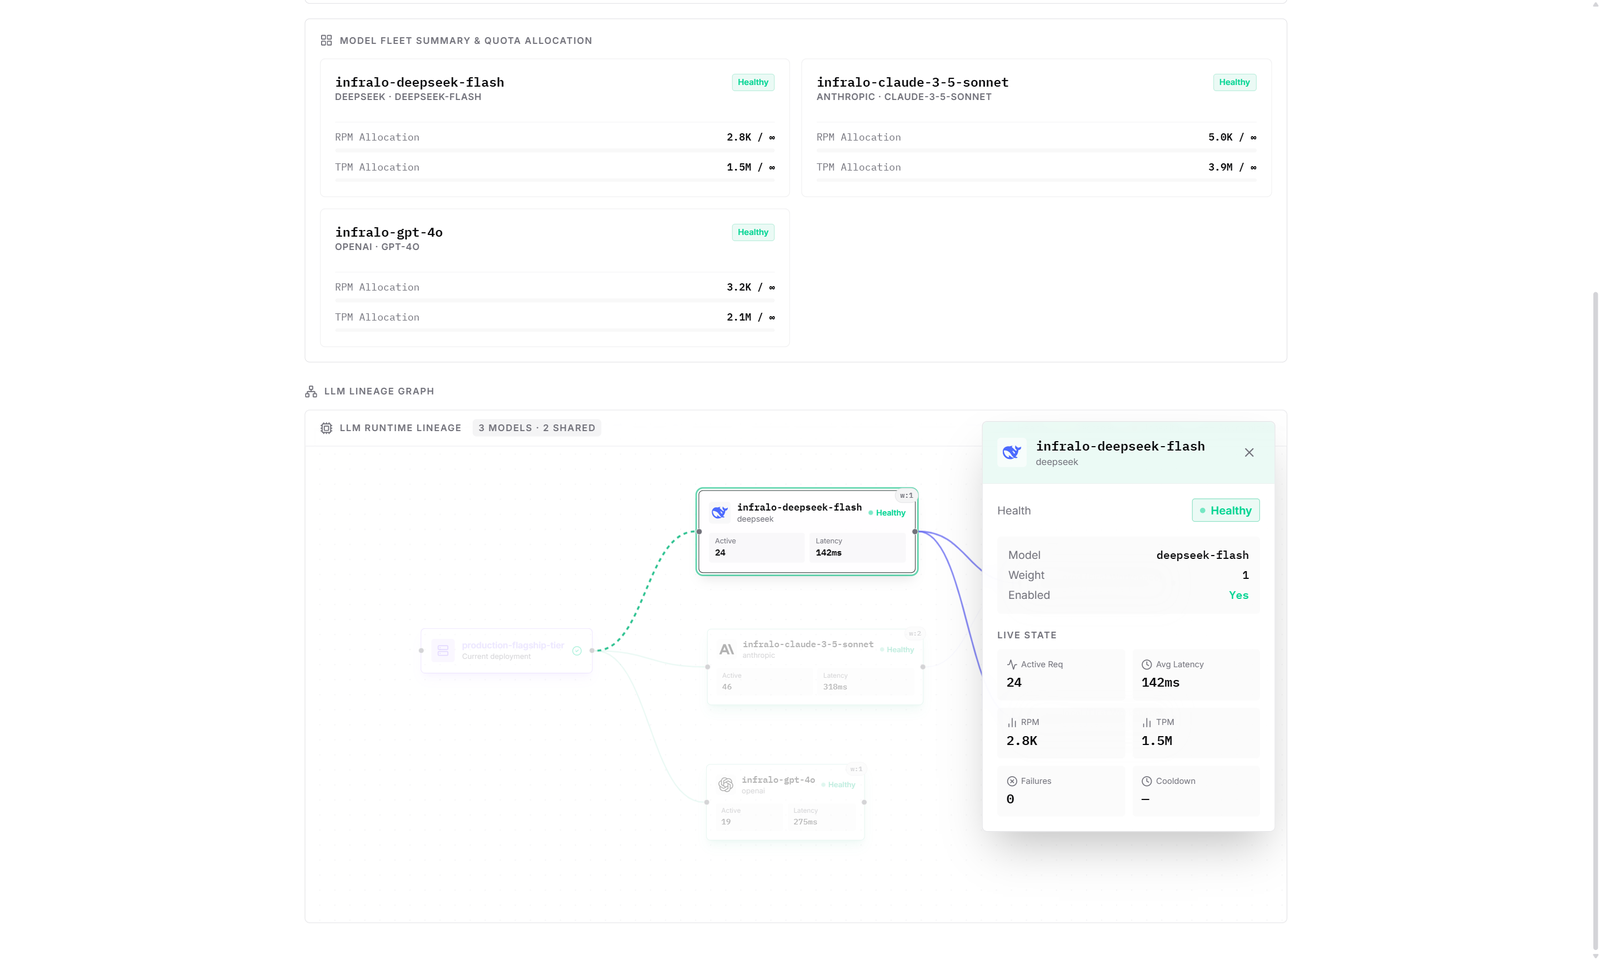
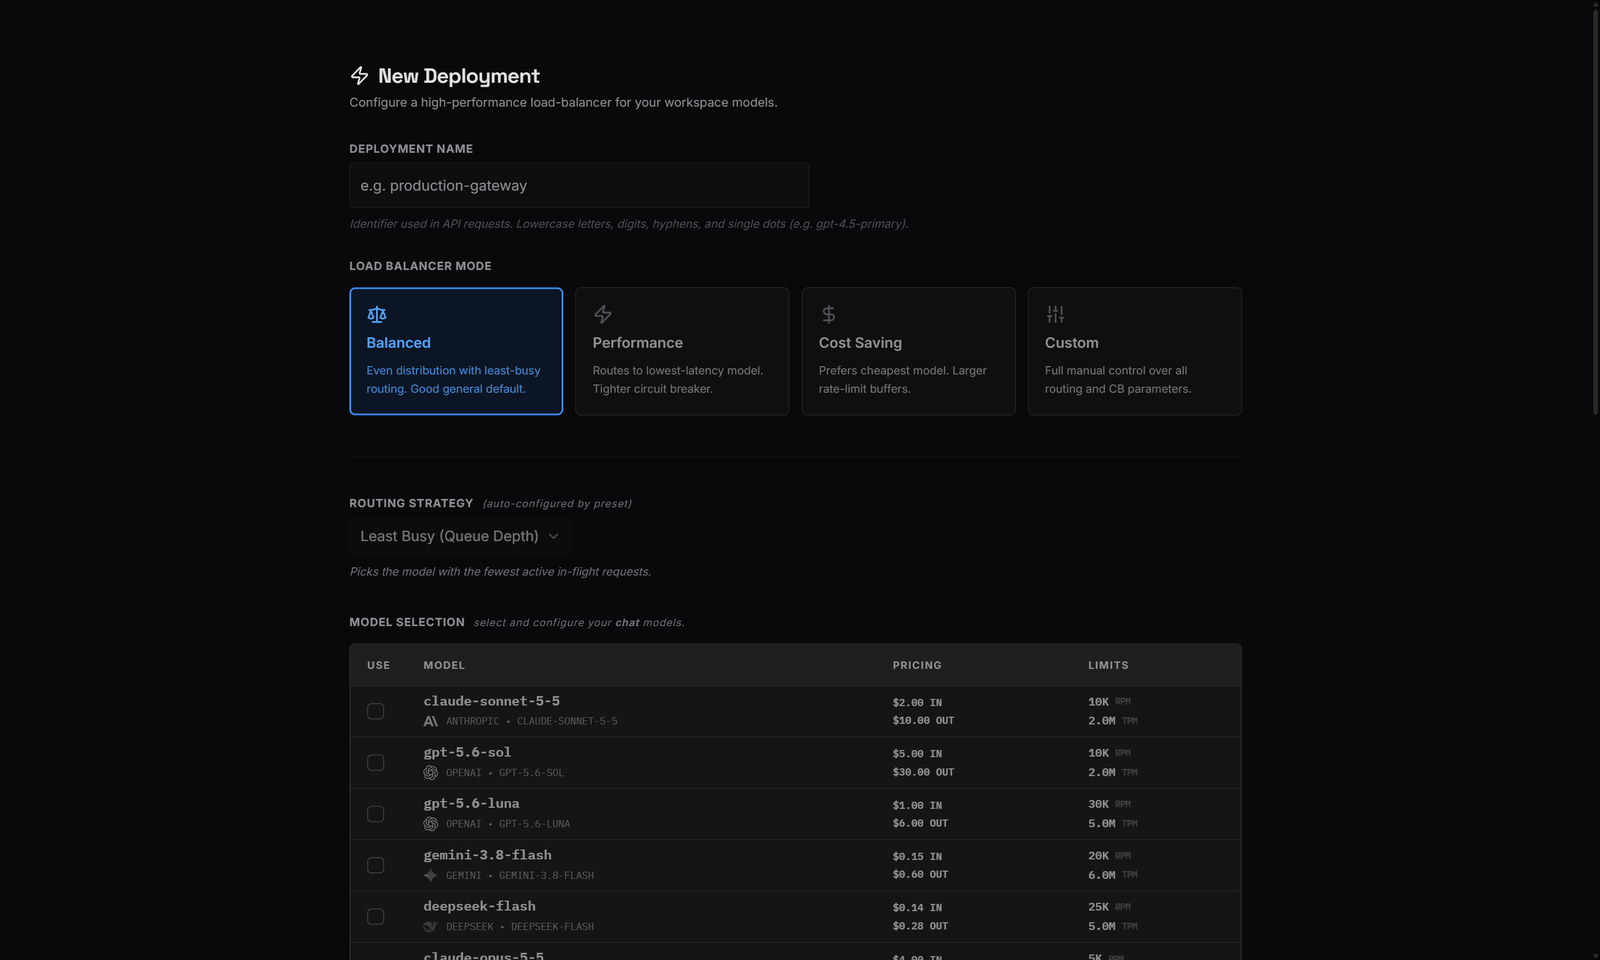
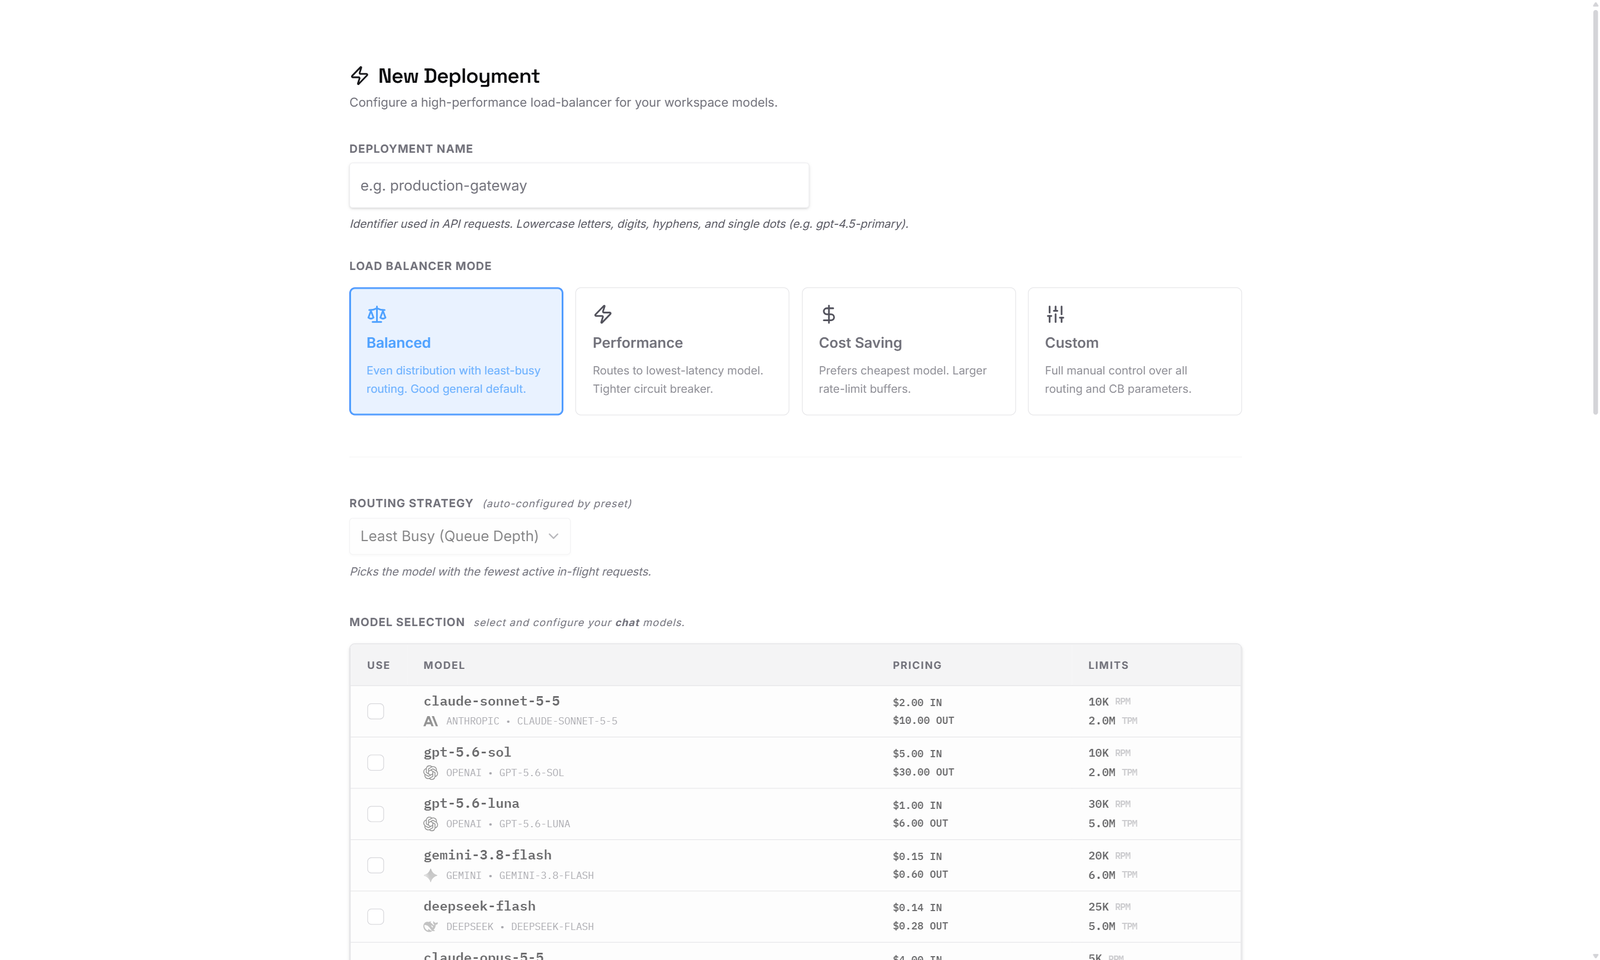
Unified virtual endpoints backed by weighted pools of upstream models. Executes zero-code pre/post interceptors (PII masking, jailbreak defense) and provides seamless sub-second failover.
- ✓ Sub-millisecond in-flight failover
- ✓ Zero-code PRE & POST pipeline
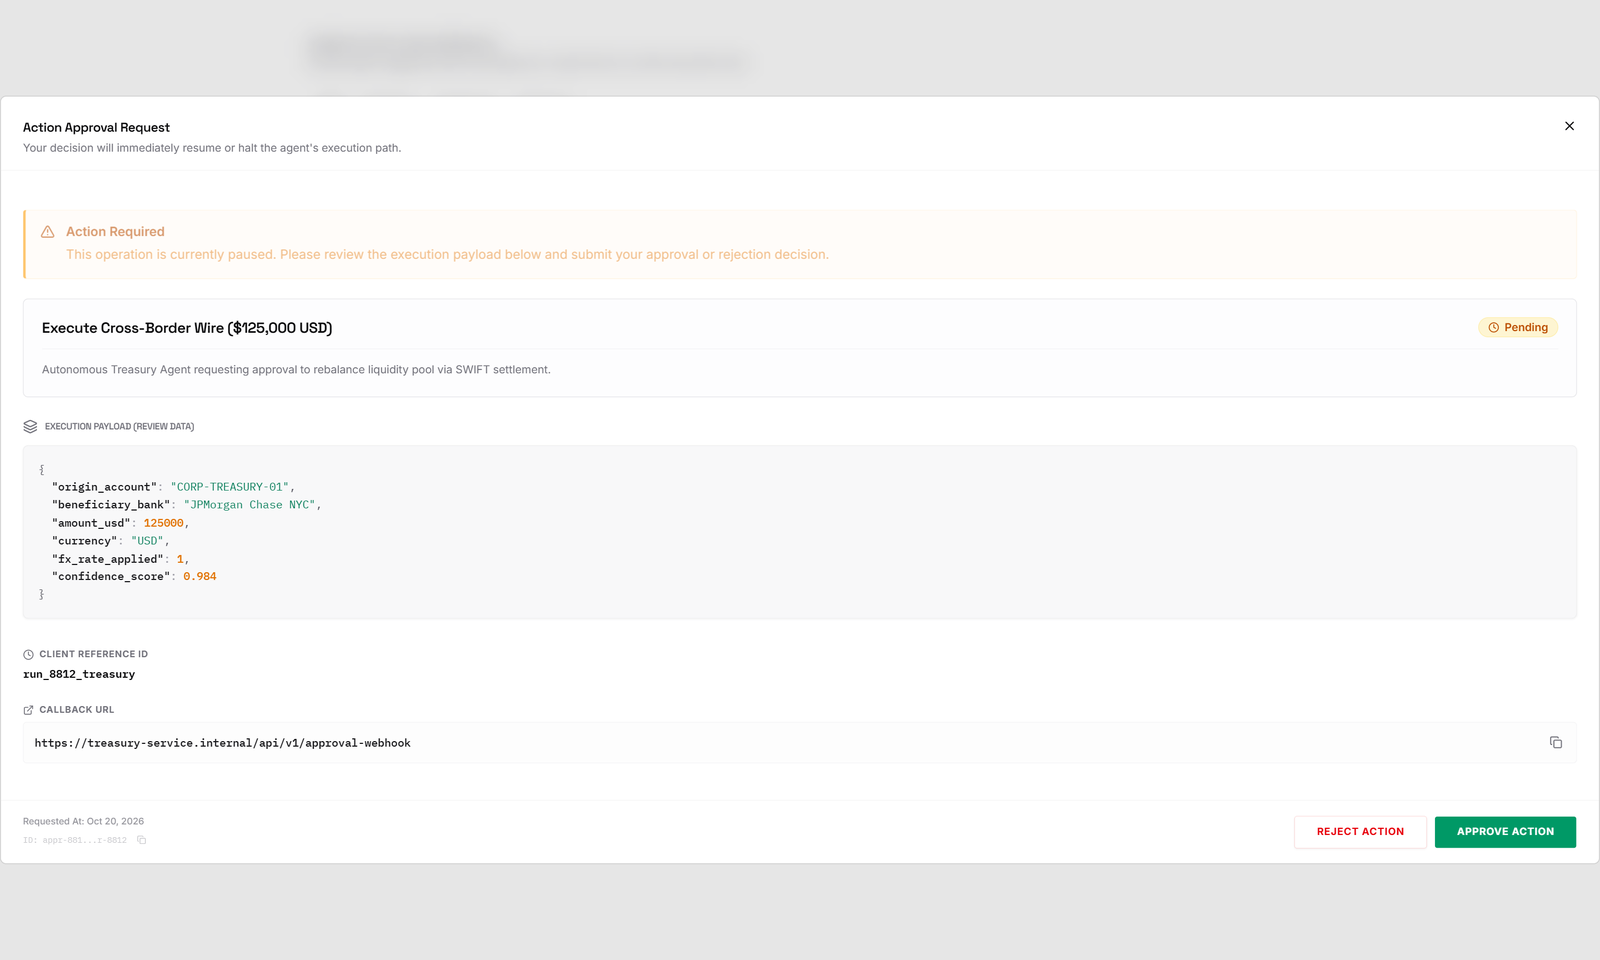
- ✓ Real-time human approval review queue
Everything required to govern enterprise AI workloads
Infralo brings battle-tested infrastructure controls to enterprise AI operations. Move from fragile direct API calls to an auditable, resilient control plane.
Zero-Code Runtime Interceptors
Bi-directional execution pipeline modules. Tokenize credit cards, IBAN, and customer PII before model transit; restore tokens on return. Block jailbreak attempts without touching application source code.
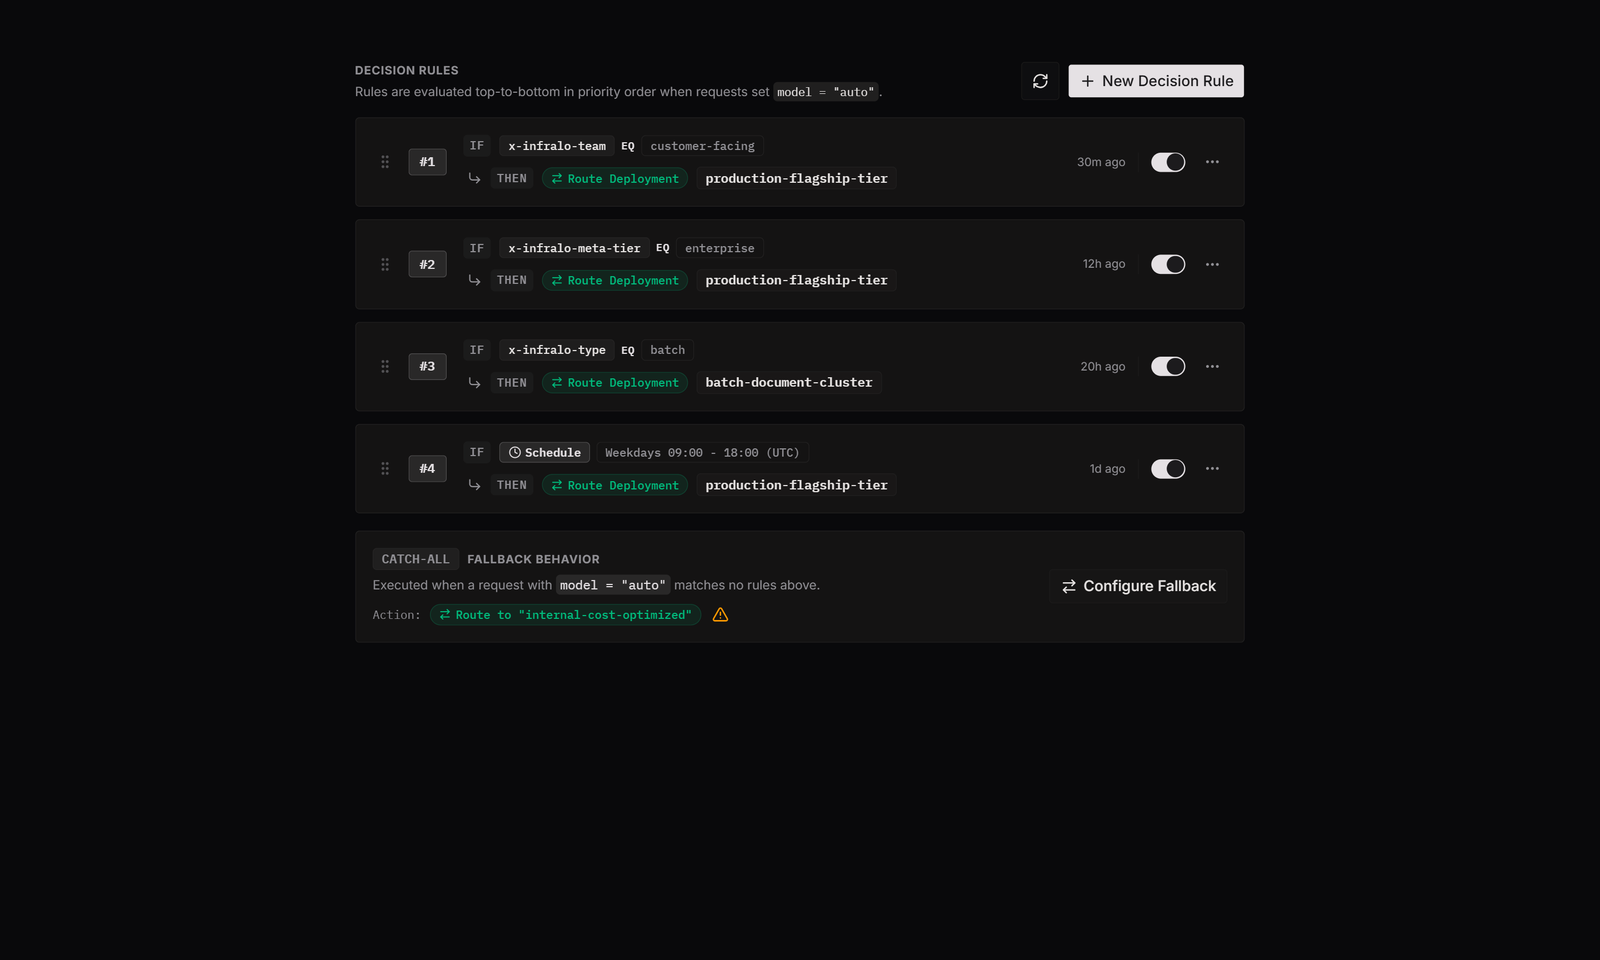
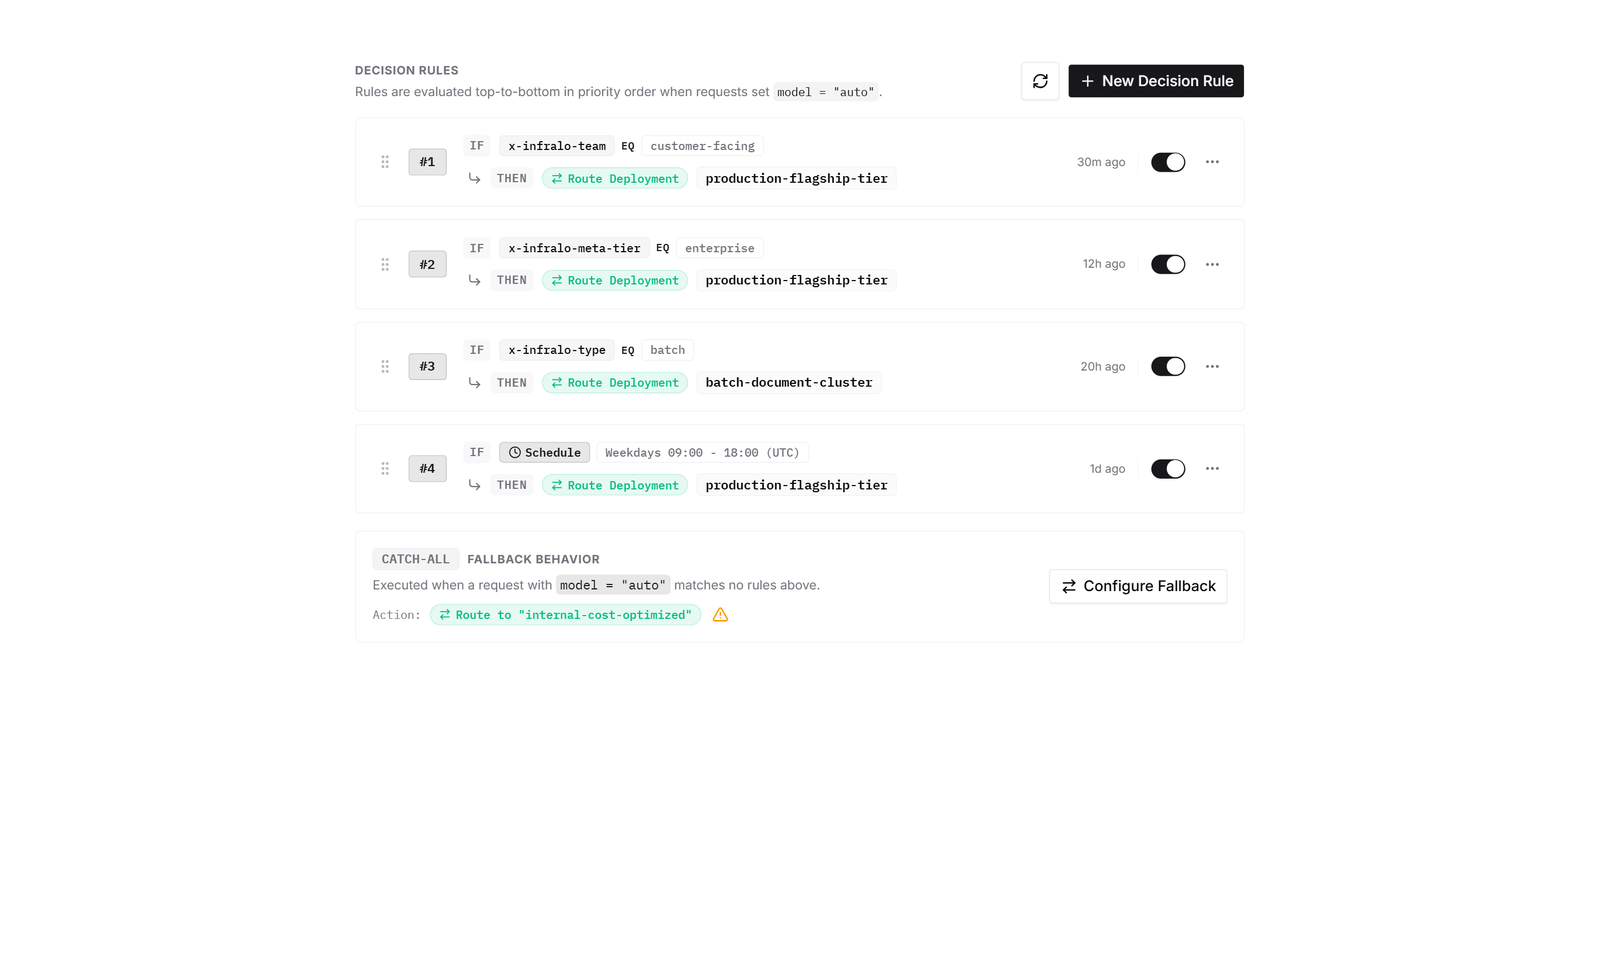
Smart Failover & Routing
Virtual deployment endpoints backing multiple upstream models. Automatic failover: if Provider A rate-limits (429) or errors (503), Infralo automatically retries Provider B in the exact same HTTP connection.
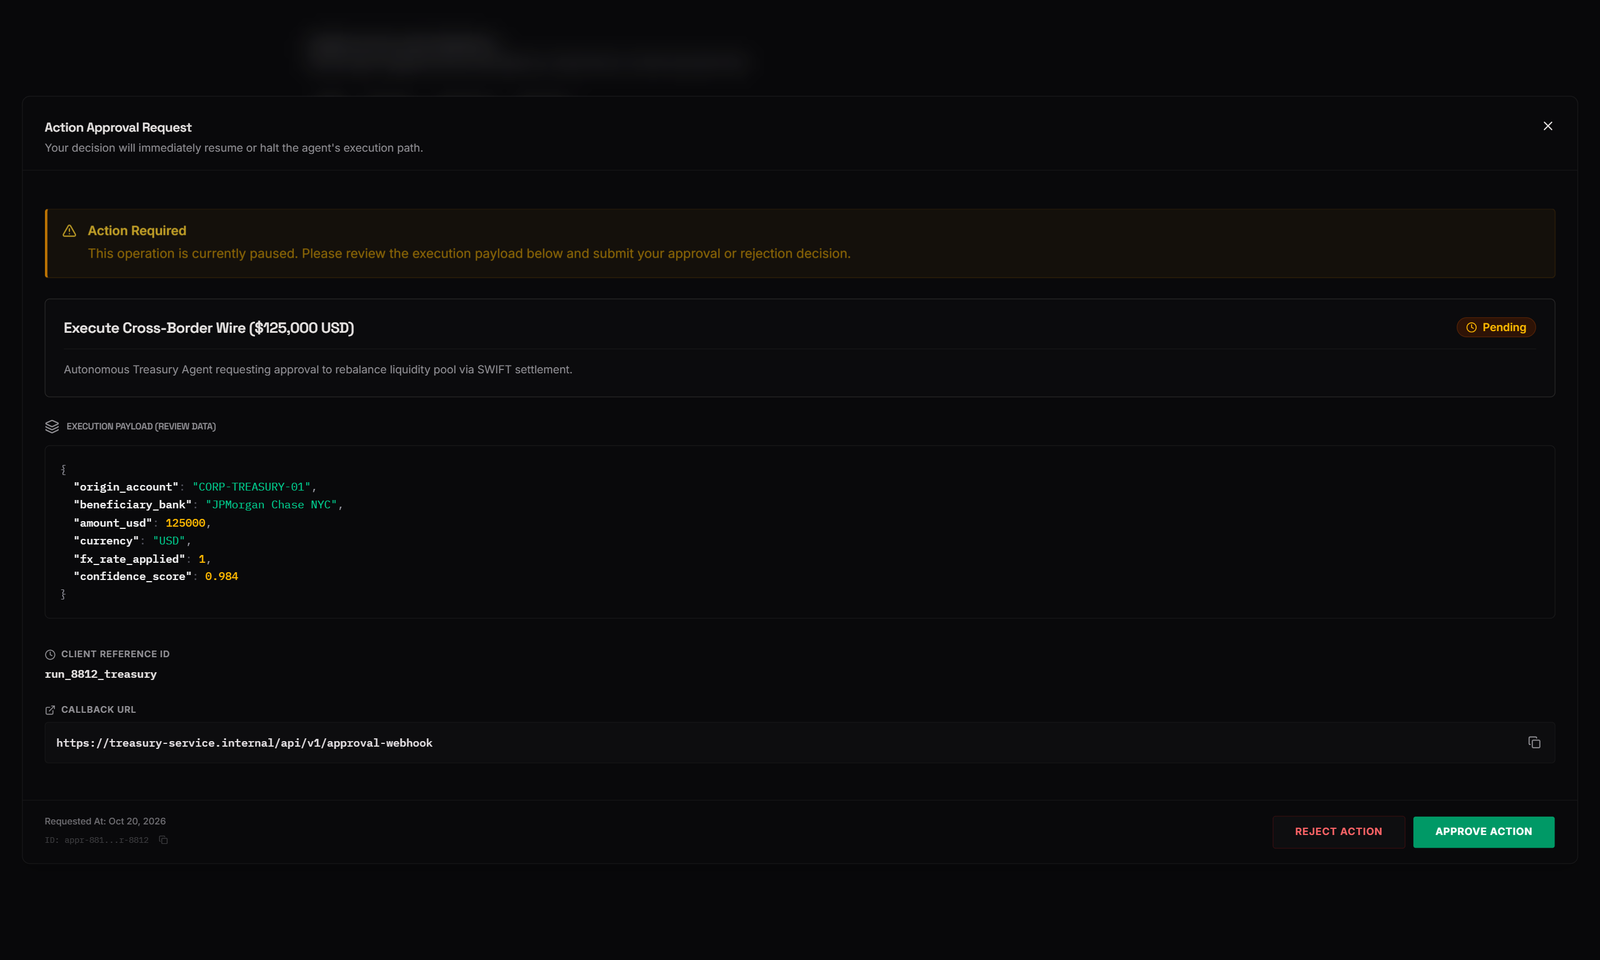
Human-in-the-Loop Approvals
Enforce mandatory human oversight on sensitive AI tool executions or agent operations. Review requests, payloads, estimated costs, and approve or reject in real time from the Control Plane queue.
Scoped Virtual Keys
Issue keys scoped to specific models, deployments, and endpoint paths with automatic expiration dates.
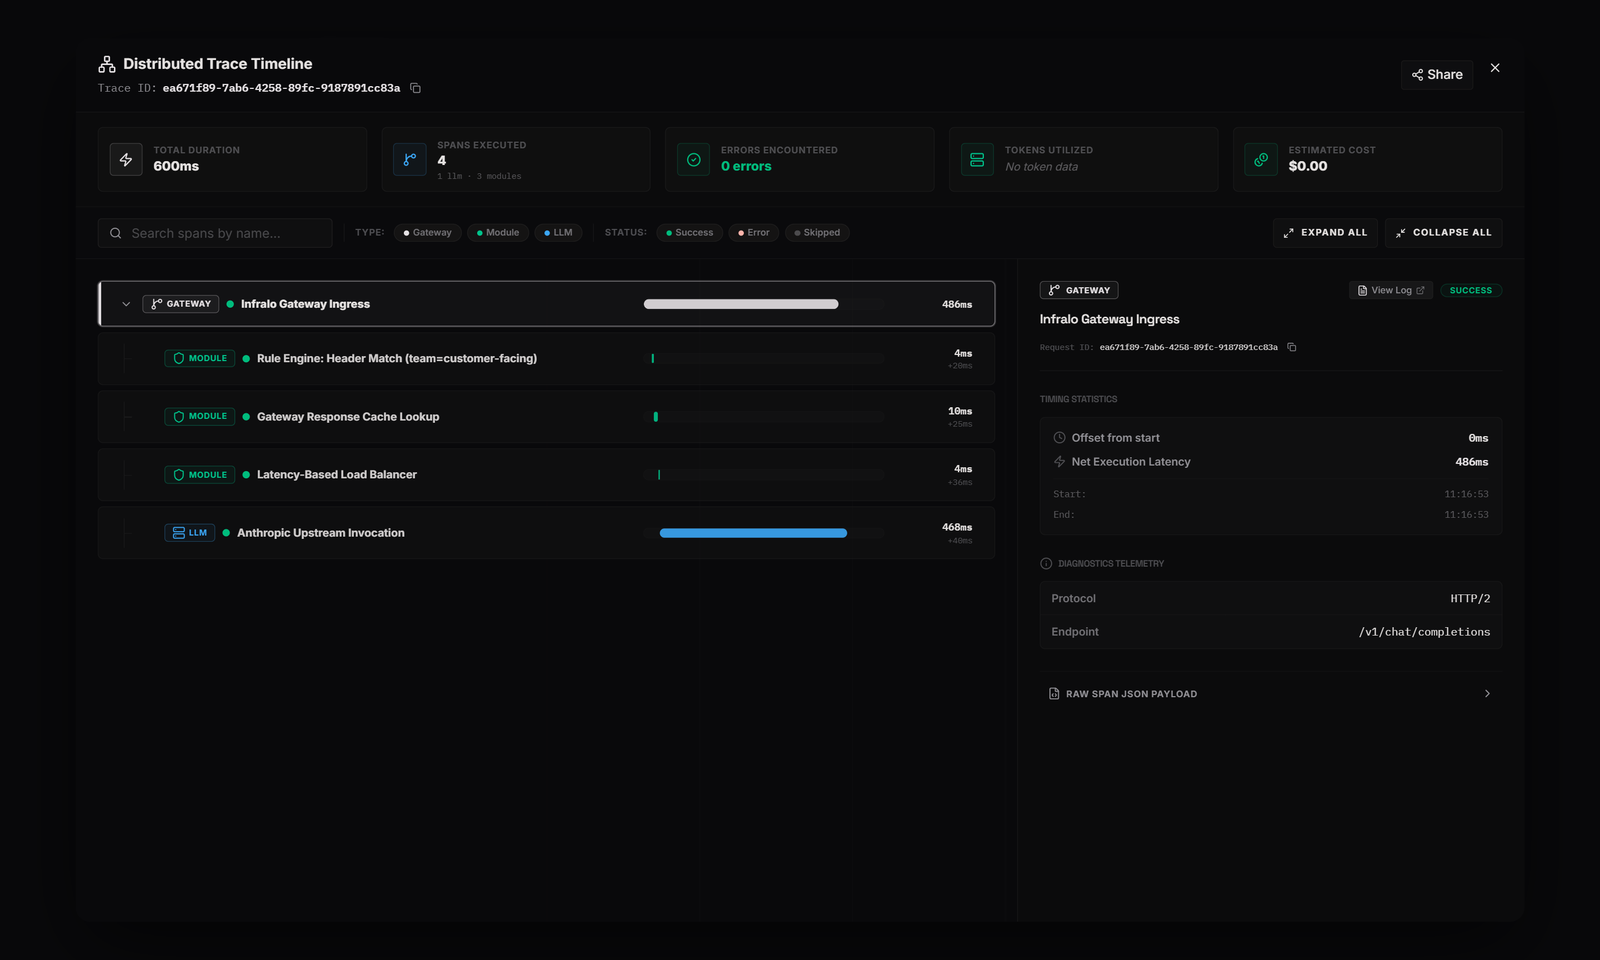
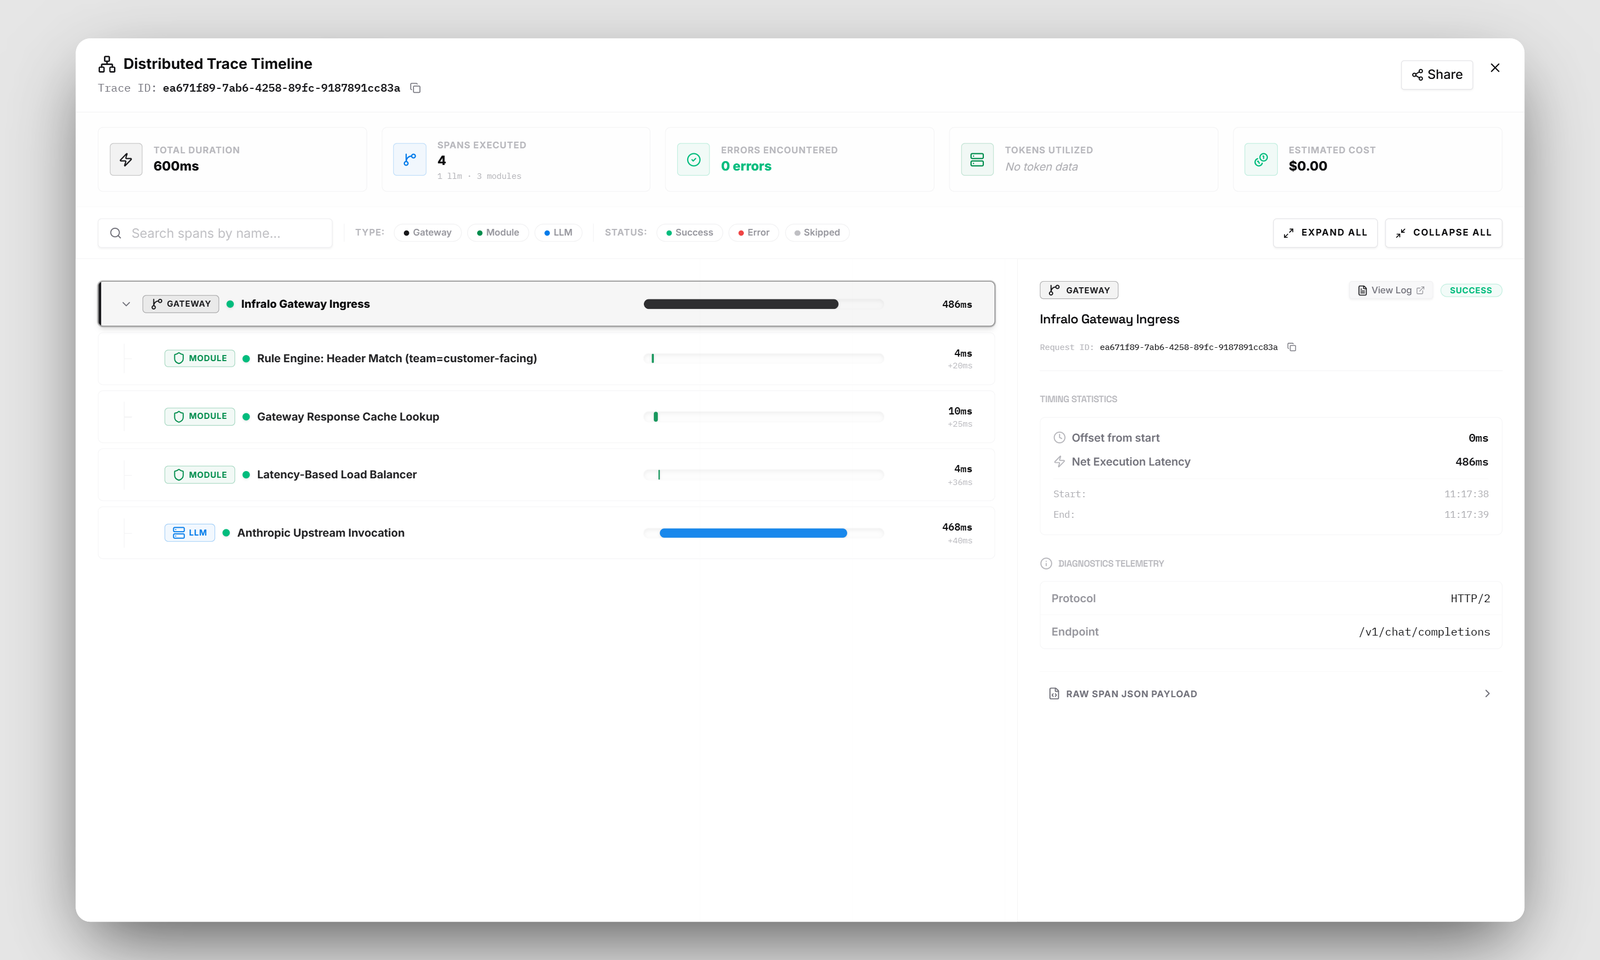
Distributed Waterfall Traces
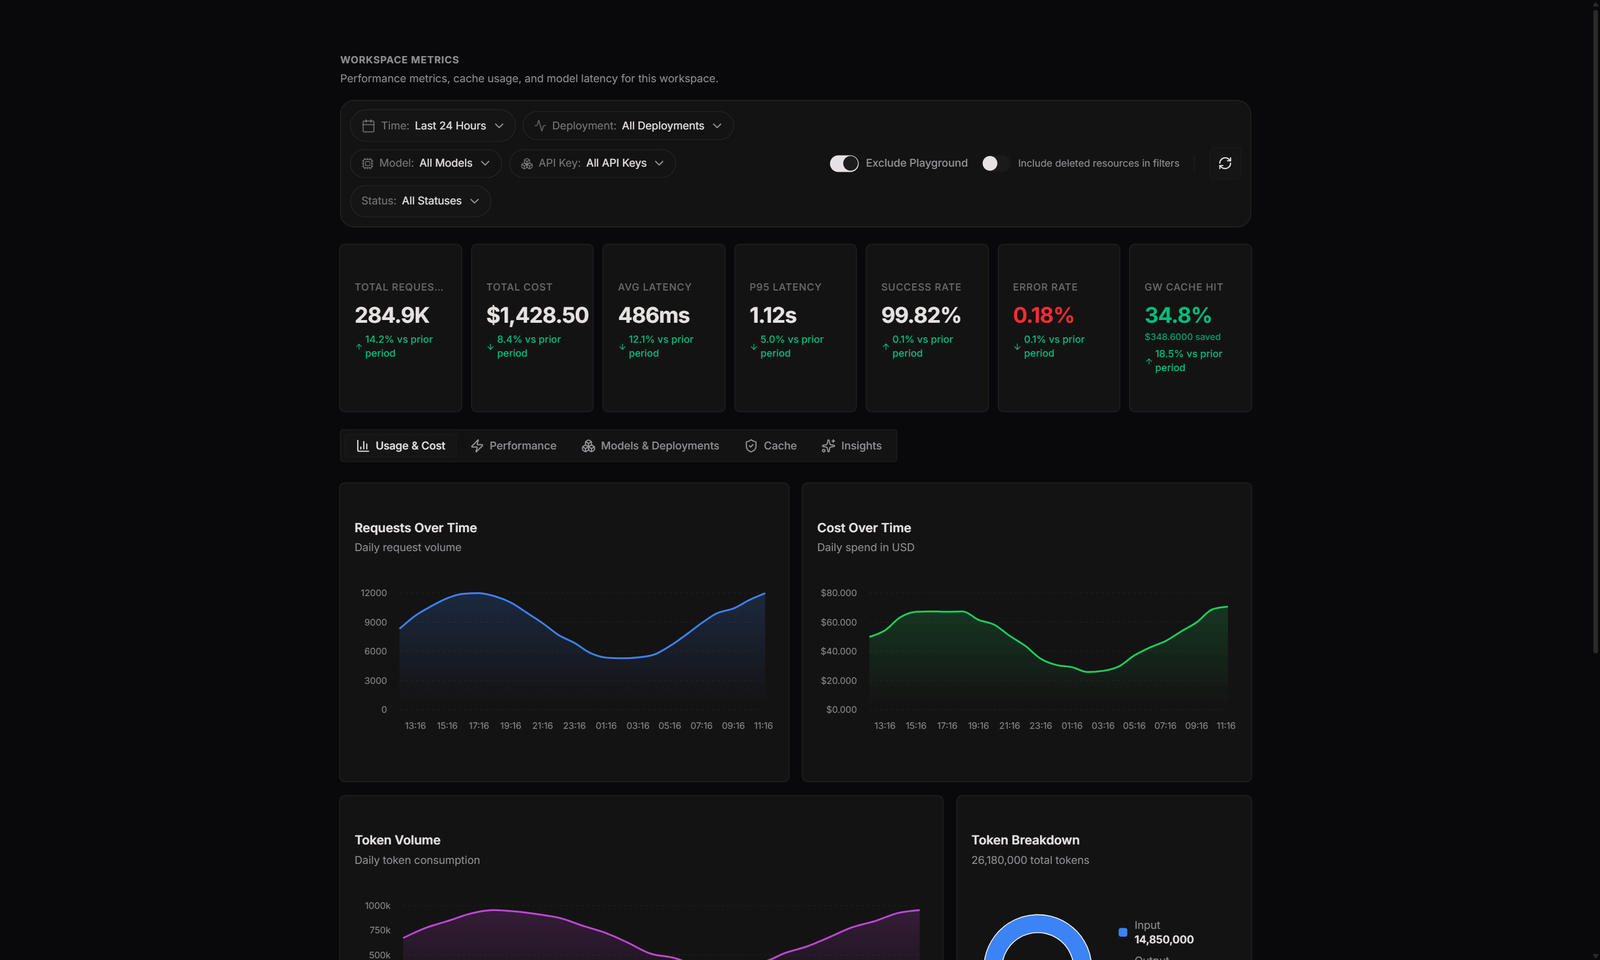
OpenTelemetry-compatible traces detailing latency across each pre-processor, upstream model, and post-processor.
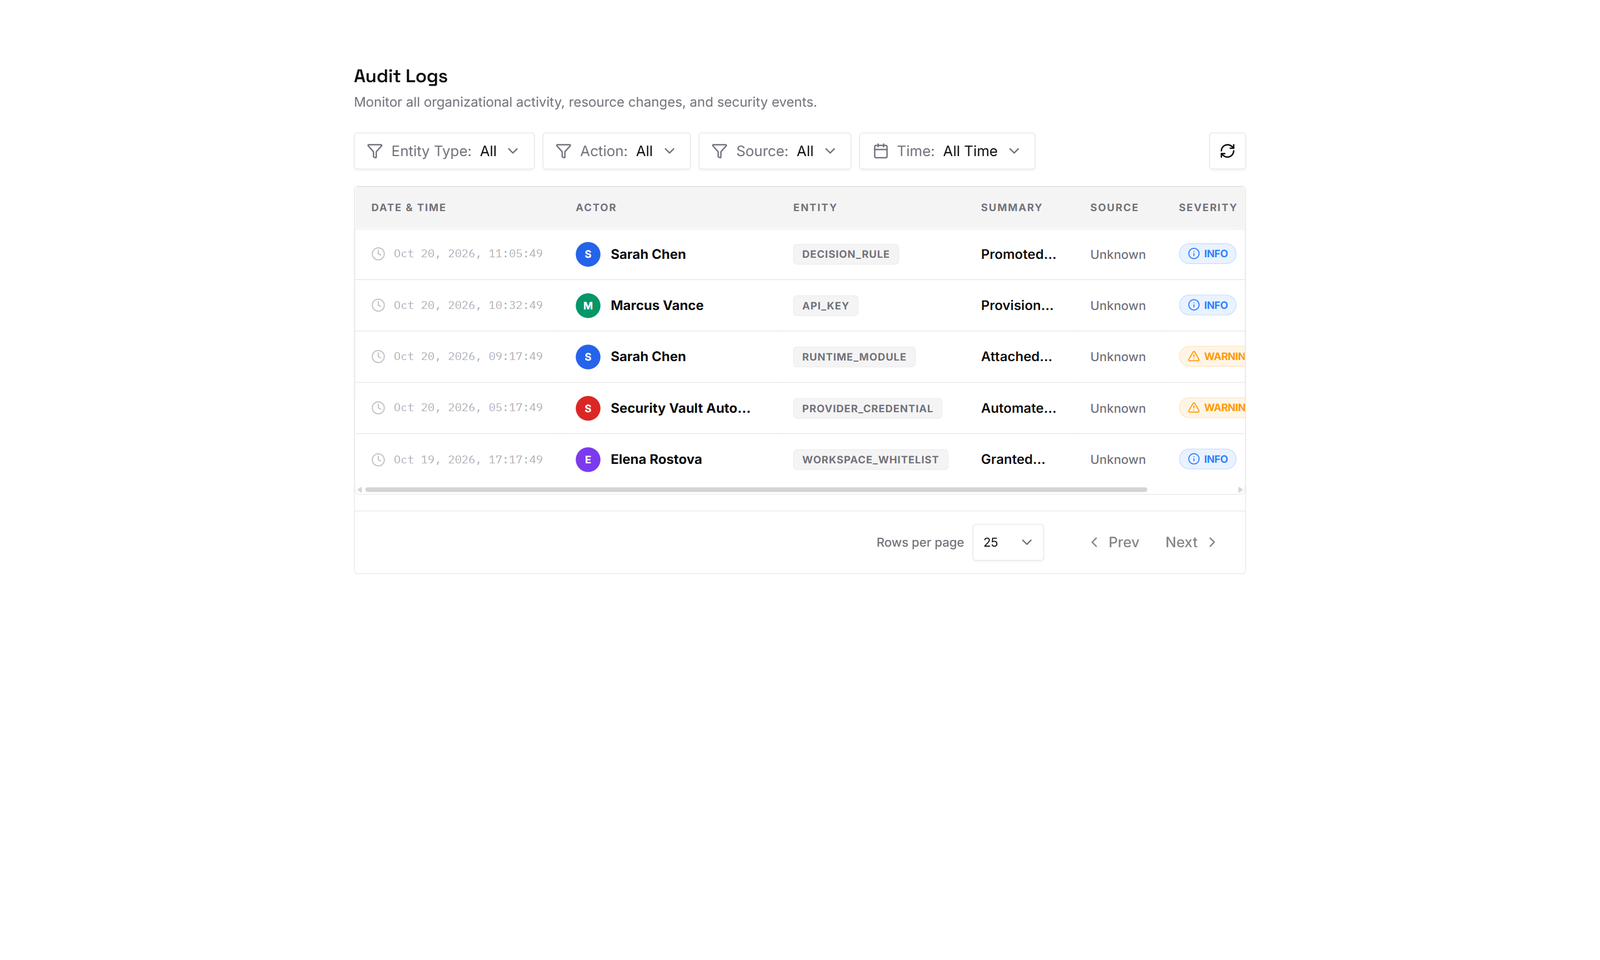
Tamper-Evident Audit Logs
Track who generated keys, changed routing rules, whitelisted models, or signed off on approvals with timestamps.
Sovereign & Air-Gapped
Run in your own VPC, Kubernetes with Helm, or on-prem air-gapped infrastructure. Your data never leaves your network.
The Four Pillars of Infralo Control Plane
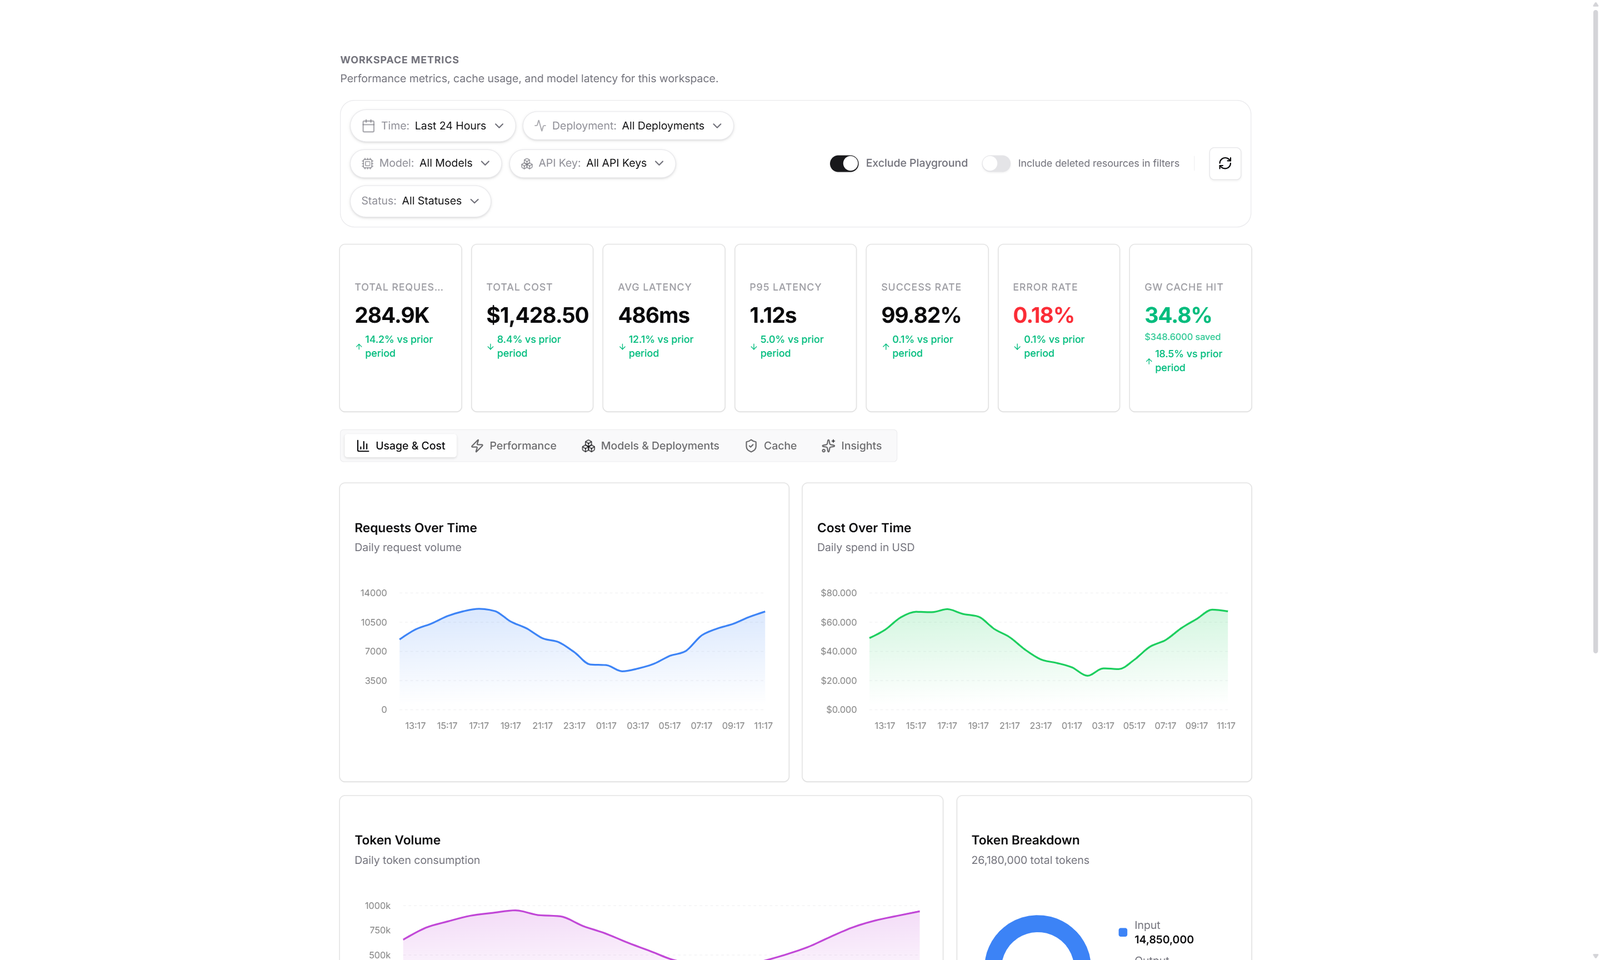
Every capability captured directly from our live enterprise frontend without artificial mockups. Explore focused interfaces across identity, assets, routing, and operational governance.
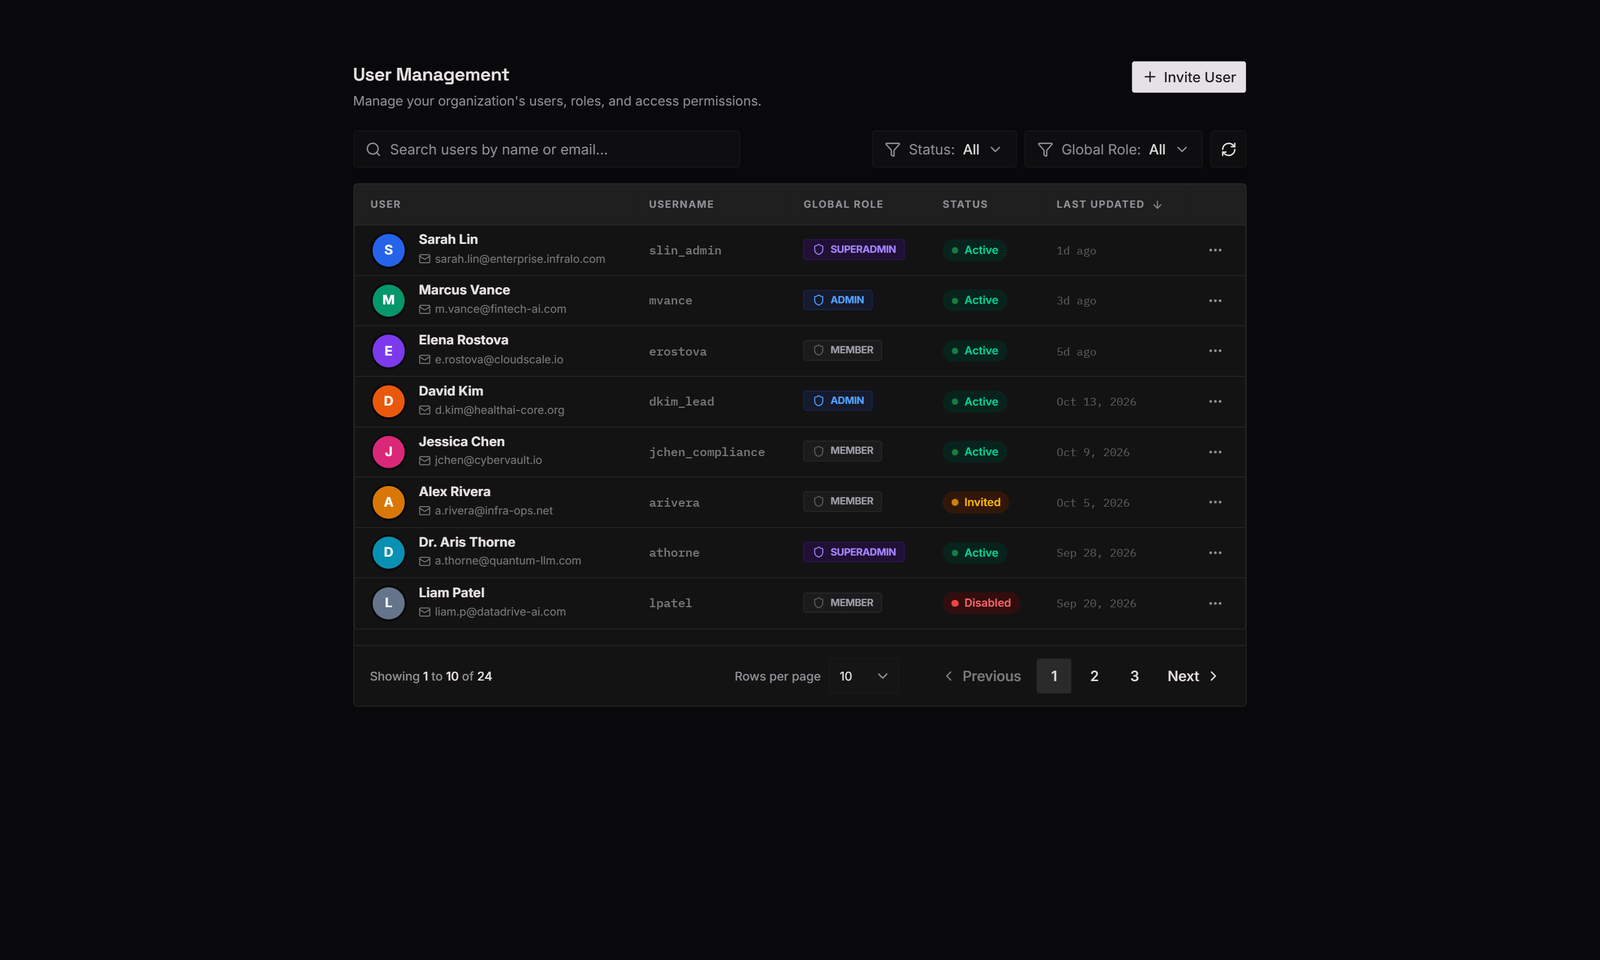
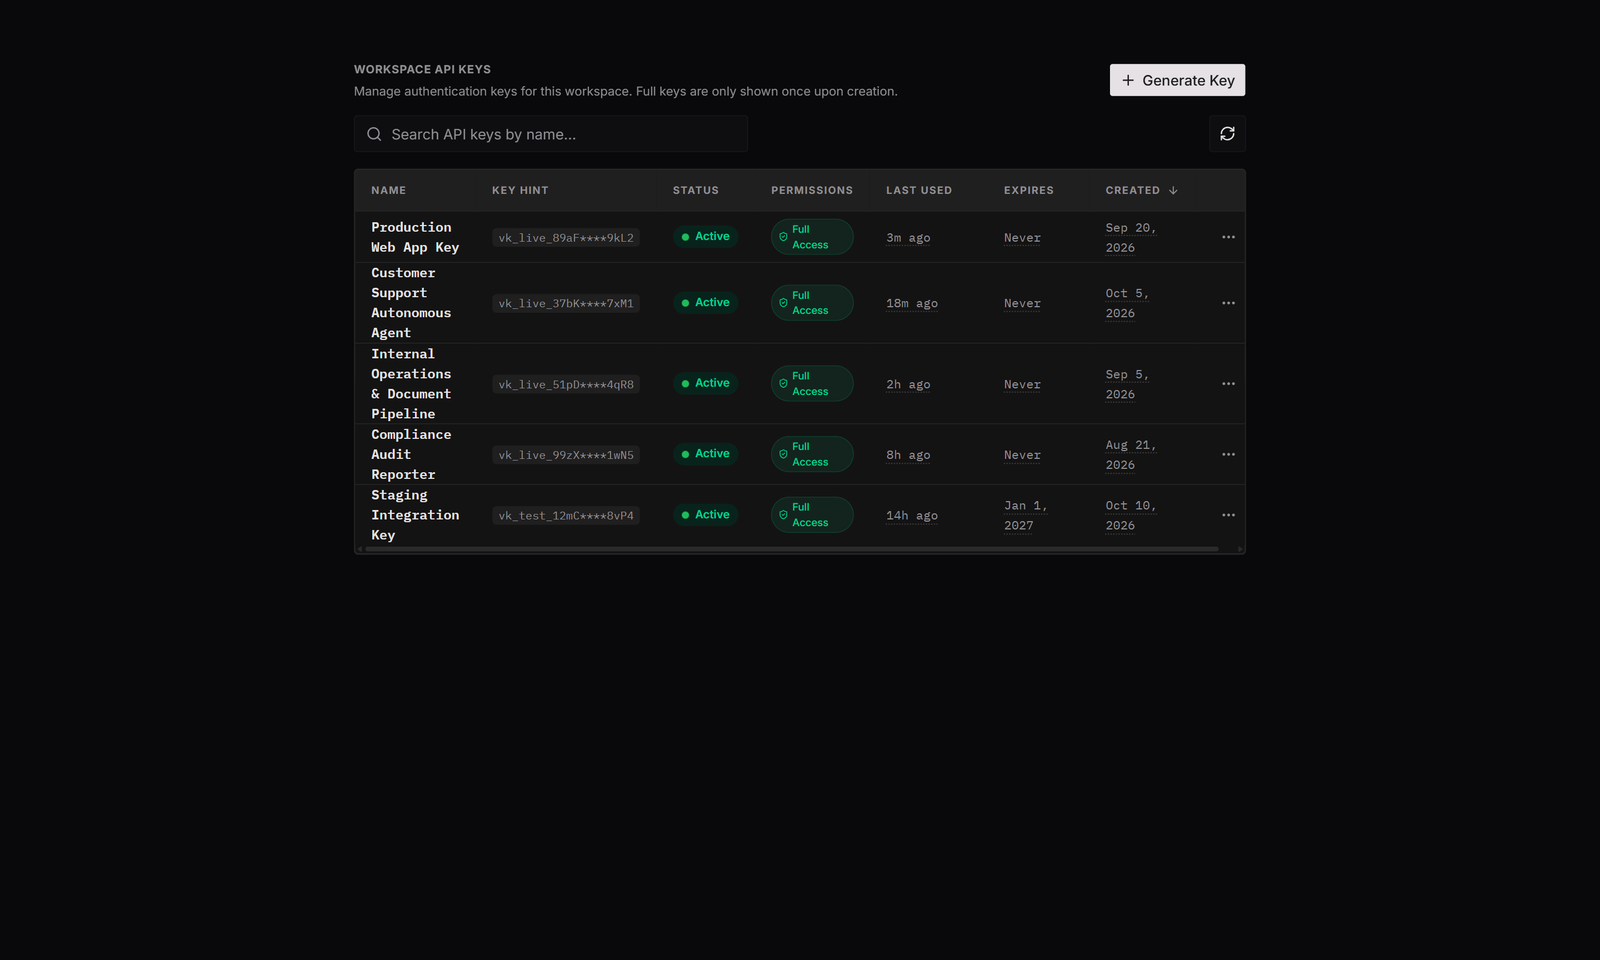
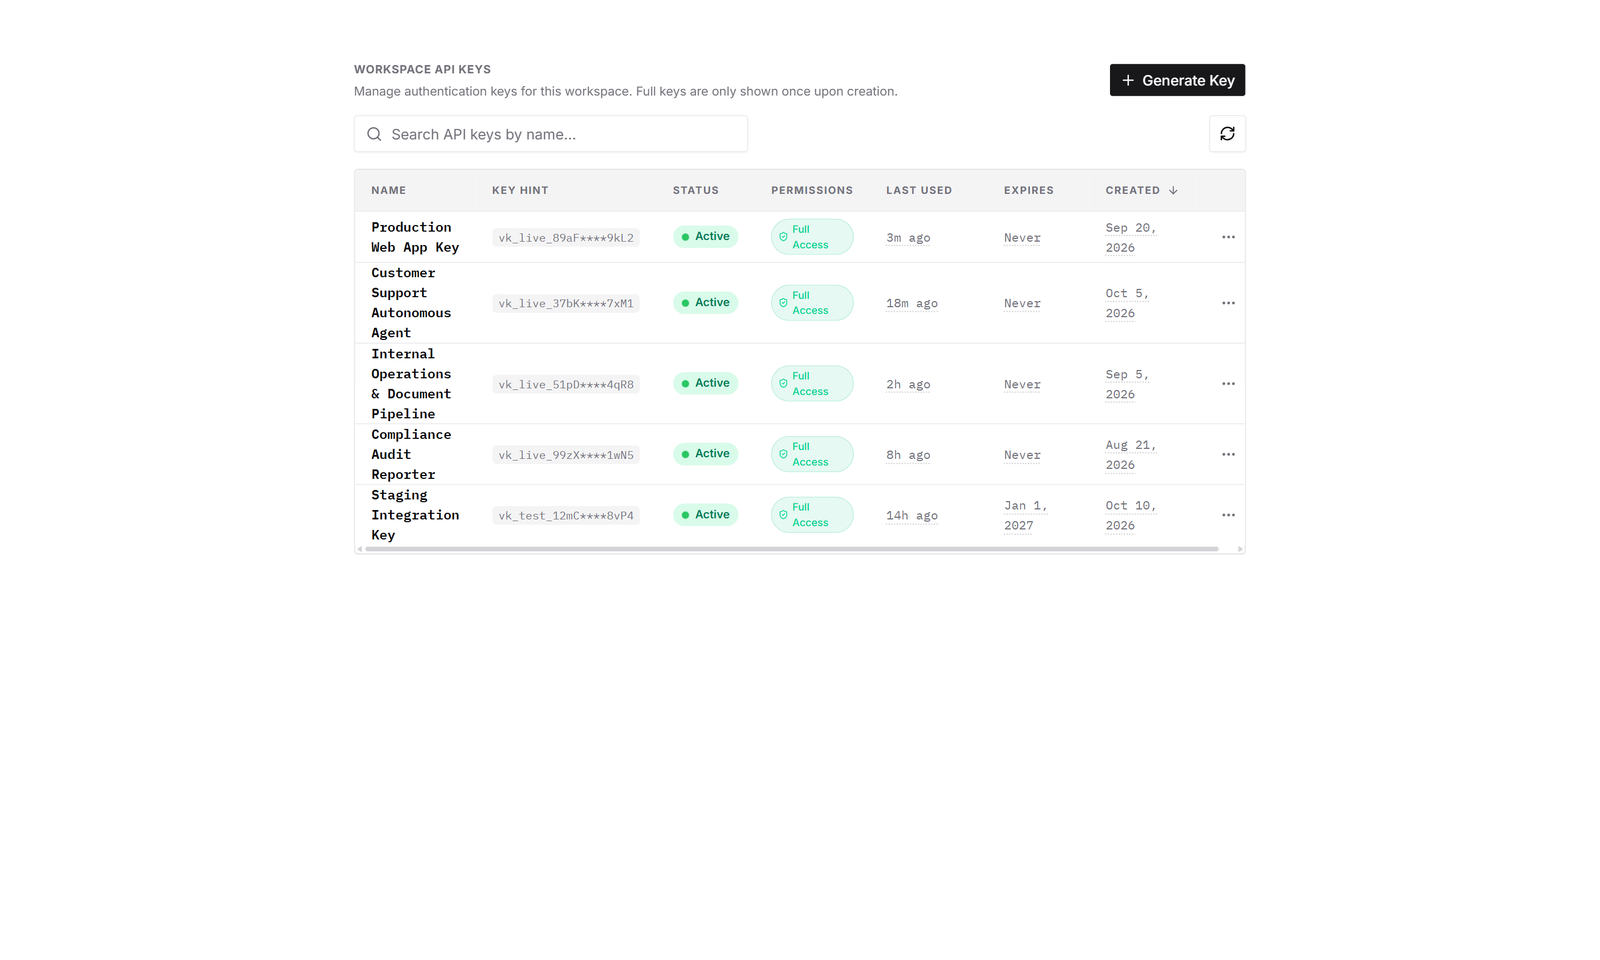
User Management, IAM Federation & Virtual API Keys
Manage organization-wide users and access boundaries from a centralized control console. Decouple backend client applications from raw upstream LLM vendor secrets, enforce granular role assignments, and issue cryptographically hashed virtual keys with granular access permissions.
User Management
Centralized user administration, global role delegation (Superadmin, Member), and instant invitation workflows.
Virtual Scoped Keys
Granular model whitelists, deployment cluster scopes, endpoint controls, and instant single-click revocation.
OIDC & SAML SSO
Federated corporate single sign-on with Okta, Azure Active Directory, and Google Workspace.
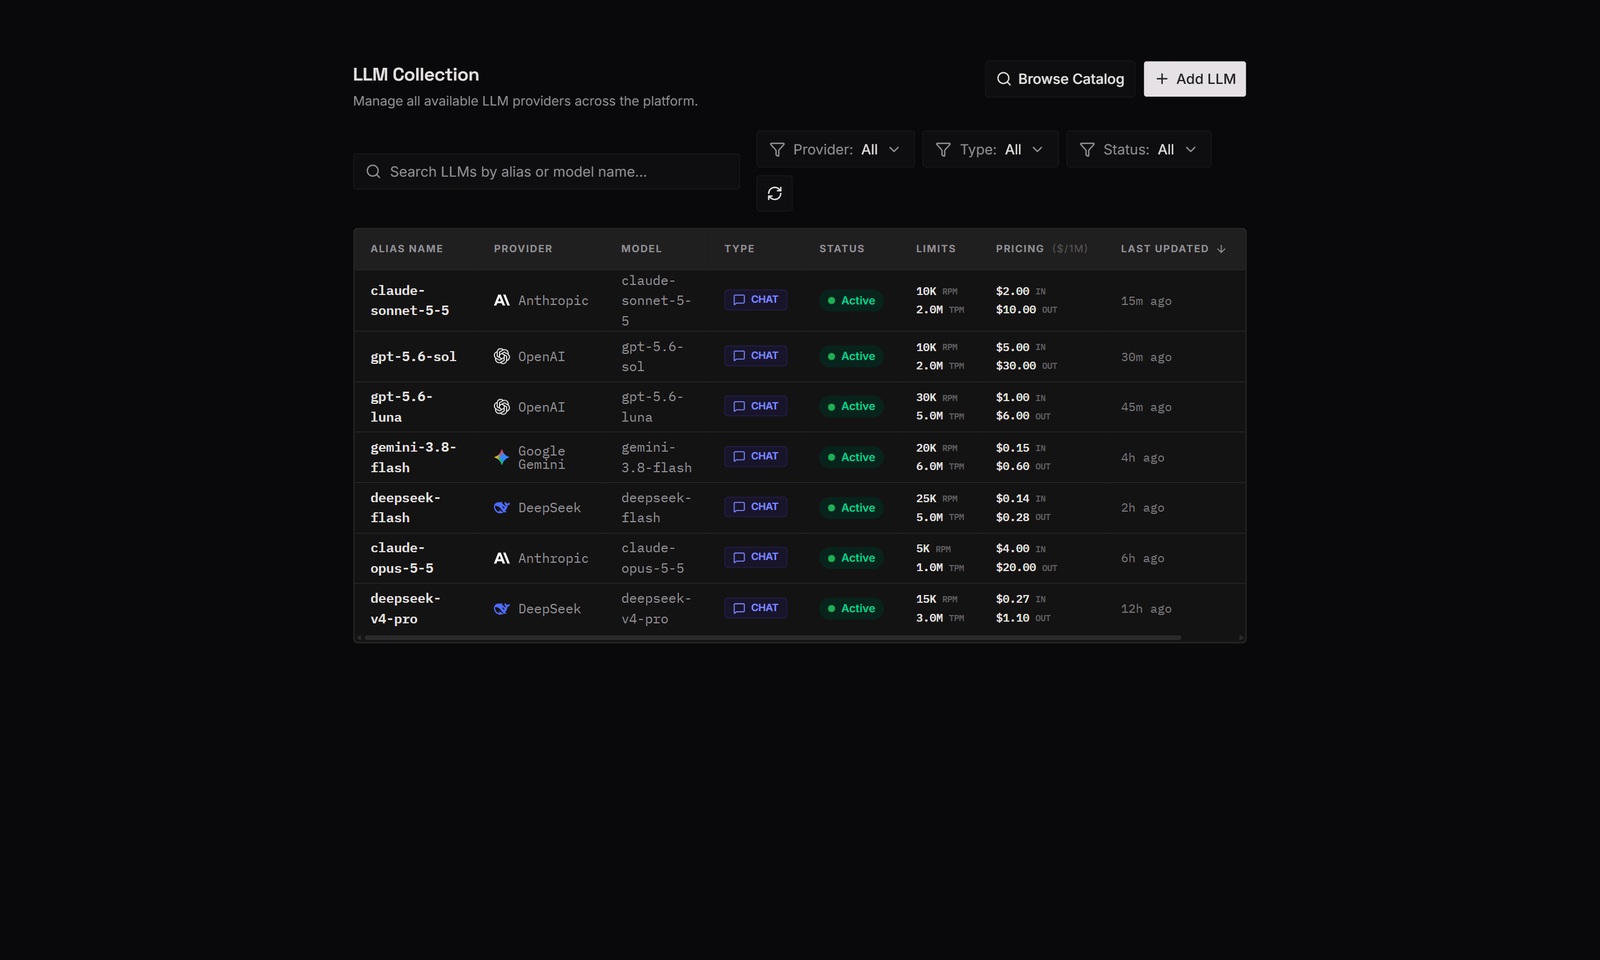
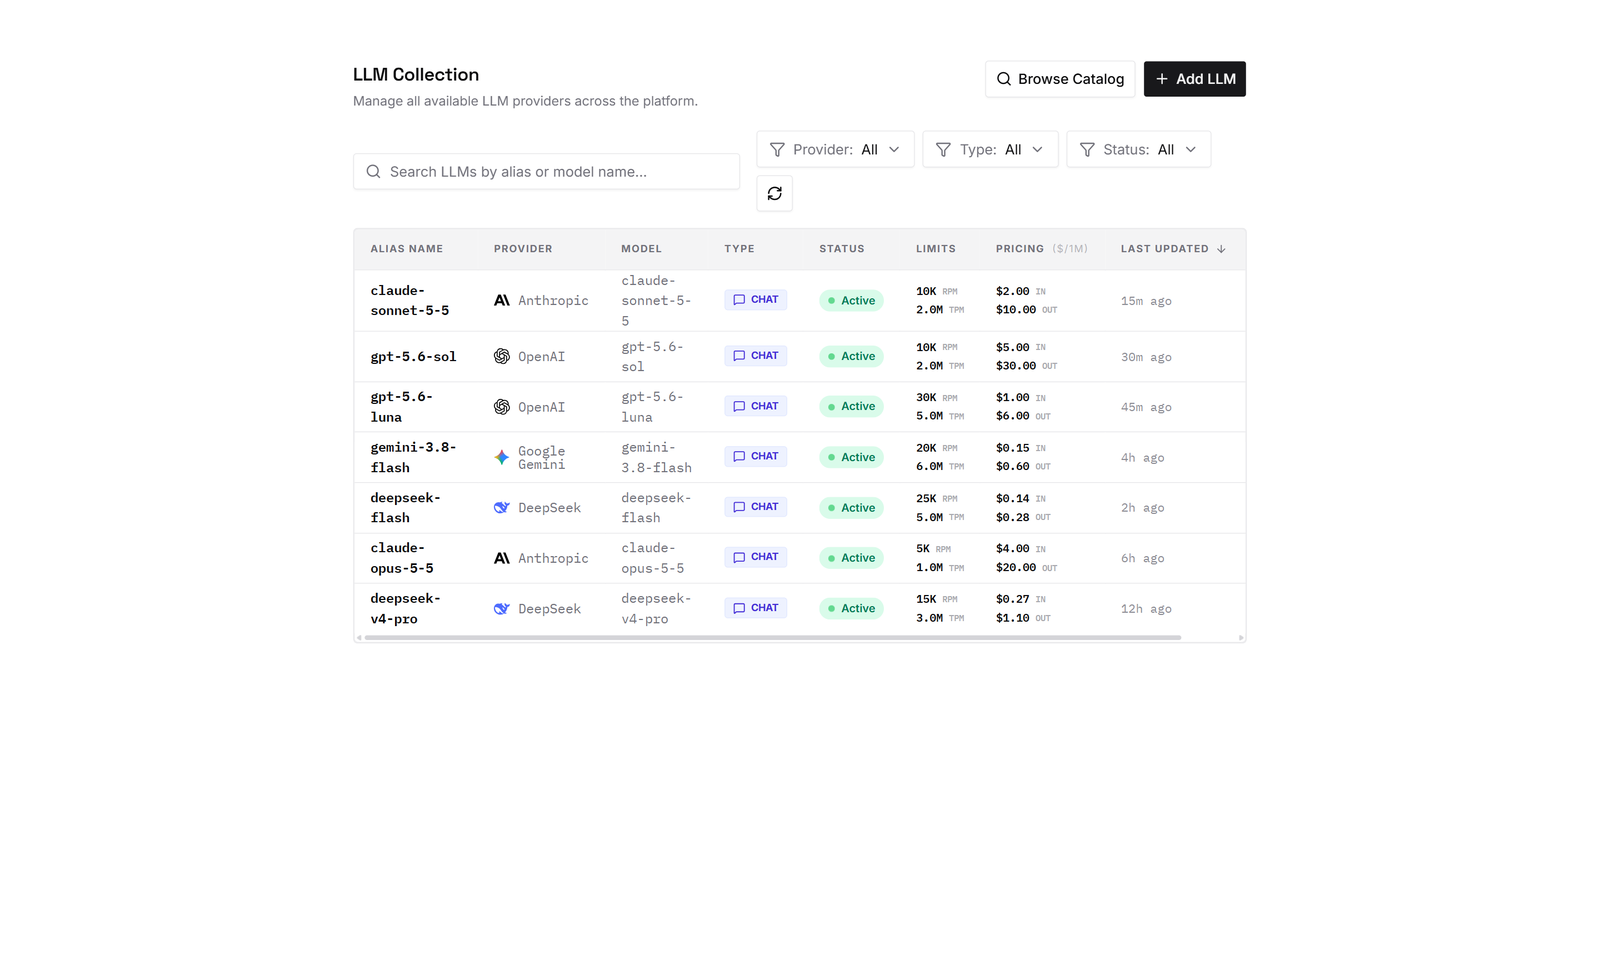
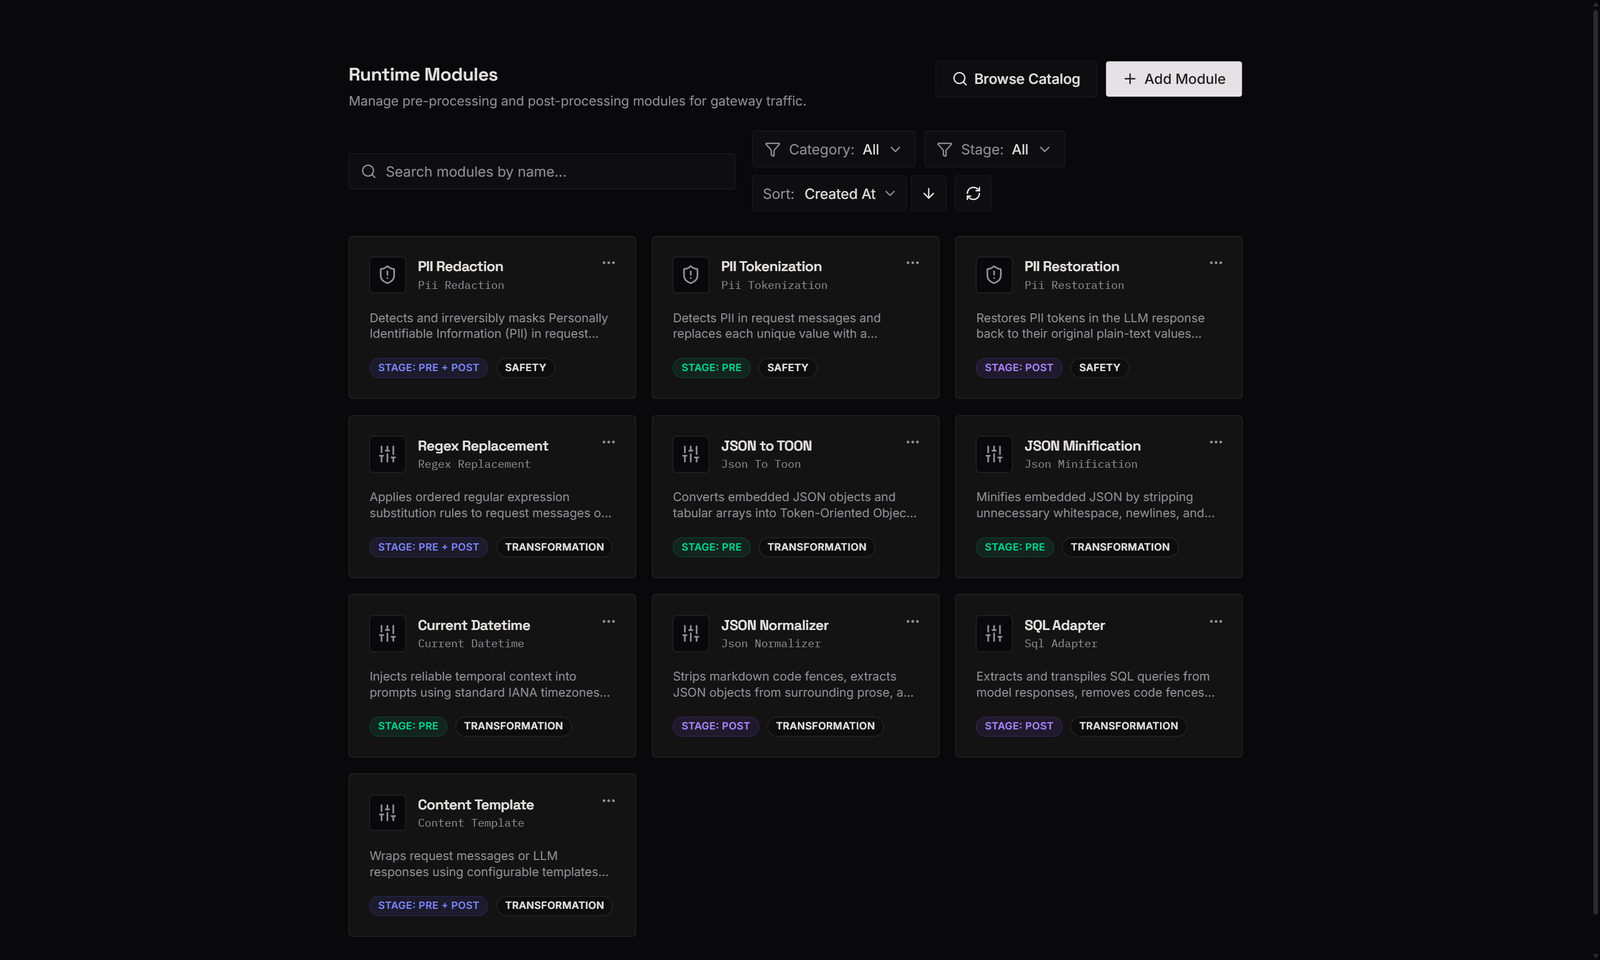
Reverse Proxy vs. Infralo Control Plane
Standard proxies forward HTTP requests and push error recovery, compliance, and secret isolation back to your application code. Infralo introduces an enterprise control plane that decouples applications from model providers with zero-trust security and automatic resiliency.
| Architecture Core Dimension | Status Quo Standard LLM Proxy Point-to-Point Forwarder |
Enterprise Layer
Infralo Control Plane
Governed Operating Mesh
|
|---|---|---|
| 01 · Security, Identity & Credential Isolation | ||
|
Provider Secret Storage
Where raw OpenAI & Anthropic keys reside
|
✕ Exposed to Applications
Raw vendor credentials distributed across client code and microservice environment variables.
|
✓ Hardware KMS Encrypted Vault
Master keys remain locked in KMS; client runtimes never touch or store raw provider tokens.
|
|
Tenancy & Organization Structure
Boundary isolation between business units
|
— Flat Namespace
Single shared account model with no cryptographic separation between teams or workspaces.
|
✓ 3-Tier Multi-Tenant Isolation
Platform, Workspace, and Deployment hierarchy with granular role-based access control (RBAC).
|
|
Client API Key Scoping
Usage quotas, path controls, and expiration
|
✕ Basic Static Tokens
Global rate limits only; no per-deployment model whitelisting or automated expiration schedules.
|
✓ Scoped Virtual Keys (vk_...)
Granular model whitelists, cluster scopes, token budget caps, and automatic key revocation.
|
| 02 · Runtime Interception & Resilient Routing | ||
|
Data Privacy & PII Guardrails
Credit card, email, and SSN sanitization
|
✕ Uninspected Plaintext
Data sent unmasked to external vendors or permanently destroyed with destructive regex.
|
✓ Reversible Pre/Post Pipeline
Pre-flight PII tokenization masks sensitive entities before transit and restores them on return.
|
|
In-Flight Failover & Circuit Breakers
Response to vendor 429s and 503 outages
|
✕ Client-Side Retry Logic
Caller application receives an HTTP error and must handle failover logic in custom code.
|
✓ Sub-1ms In-Flight Failover
Seamlessly switches to healthy secondary providers within the exact same active HTTP connection.
|
|
Human-in-the-Loop Approvals
Supervisor sign-off for sensitive operations
|
— Unsupported
All model tool calls execute blindly without approval barriers or human intervention.
|
✓ Real-Time Approval Queue
Asynchronously pauses execution, notifies reviewers via webhook/Slack, and resumes on sign-off.
|
| 03 · Observability & Infrastructure Sovereignty | ||
|
Distributed Tracing & Telemetry
Visibility into per-hop latency bottlenecks
|
— Counter Metrics Only
Gross request counts and aggregated token totals without per-hop span breakdown.
|
✓ Multi-Span Waterfall Telemetry
Sub-millisecond latency breakdown across Ingress, Guardrails, Cache, and Model execution.
|
|
Audit Trail & Governance Logs
Traceability of all administrative changes
|
✕ Ephemeral Server Logs
Standard rotated server logs without structured actor identity attribution or policy diffs.
|
✓ Tamper-Evident Audit Trail
Immutable structured records of all key creations, policy updates, and approval decisions.
|
|
Deployment Sovereignty
Data residency and infrastructure control
|
— Shared Multi-Tenant SaaS
All company inference traffic must route through shared third-party proxy hosts.
|
✓ Air-Gapped VPC & Kubernetes
Deploy self-hosted in your AWS/GCP VPC, Bare Metal, or sovereign private cloud environments.
|
Drop-In Compatibility.
Zero Codebase Rewrites.
Keep your existing client libraries and agent frameworks. Point your client's base_url
to Infralo and pass your workspace Virtual Key (vk_...).
from openai import OpenAI

# Virtual Key issued & governed by Infralo Control Plane
client = OpenAI(
    api_key="vk_live_enterprise_8f902ba1",
    base_url="https://controlplane.infralo.com/api/v1"
)

# Route requests with sub-1ms failover & policy guardrails
response = client.chat.completions.create(
    model="production-flagship-tier",
    messages=[
        {"role": "system", "content": "Enterprise financial analytics engine"},
        {"role": "user", "content": "Summarize customer account statements"}
    ]
)

# In-flight PII masking and audit logs applied automatically
print(response.choices[0].message.content)Frequently Asked Questions
base_url
to your Infralo Control Plane and authenticate using your workspace virtual key.
Ready to establish enterprise AI governance?
Centralize your models, decouple credentials, enforce runtime guardrails, and secure your AI infrastructure today.